GMP Audit Archives | GxP Cellators Consultants Ltd.

14/10/2026
GMP-Compliance-Gaps-Regulators-1280x720.webp

Introduction

Good Manufacturing Practices (GMP) play an important role in pharmaceutical manufacturing, product quality, and patient safety. Pharmaceutical companies must follow applicable GMP requirements to ensure that products are consistently manufactured, tested, documented, and controlled according to established quality standards.

However, even organizations with established quality management systems can experience compliance issues. Inadequate documentation, data integrity weaknesses, ineffective deviation investigations, poor supplier management, and incomplete employee training can create risks during regulatory inspections.

In 2026, pharmaceutical companies should pay particular attention to these areas when reviewing their compliance programs. Although specific findings vary by facility, product, and regulatory authority, several recurring weaknesses can affect inspection readiness.

Understanding these GMP compliance gaps helps organizations identify problems early and implement effective corrective and preventive actions (CAPA). GxP Cellators provides GMP auditing services to help pharmaceutical organizations evaluate their quality systems, identify potential gaps, and strengthen regulatory compliance.

What Are GMP Compliance Gaps?

GMP compliance gaps are differences between applicable regulatory requirements and an organization’s existing procedures, practices, documentation, or quality controls.

These gaps may develop because of outdated procedures, inadequate training, ineffective oversight, equipment issues, or weaknesses in quality management systems.

For example, a pharmaceutical company may have a written procedure for investigating deviations. However, if investigations do not identify the underlying causes of recurring problems, the procedure may not be effective in practice.

Similarly, a facility may maintain electronic records but fail to implement appropriate access controls or audit trail reviews. Such weaknesses can create data integrity risks.

Regular GMP compliance audits help organizations identify these problems, evaluate their potential impact, and prioritize corrective actions before they become more serious compliance concerns.

1. Data Integrity and Electronic Record Management

Data integrity remains a critical area of pharmaceutical quality management. Regulatory expectations require records and data used in regulated activities to be reliable, accurate, complete, and appropriately maintained throughout their lifecycle.

Common data integrity issues include shared user accounts, inappropriate access permissions, incomplete audit trail reviews, missing records, and undocumented changes to electronic data.

These weaknesses can affect laboratory testing, manufacturing operations, quality control, and batch release decisions.

How to Address Data Integrity Gaps

Pharmaceutical companies can strengthen data integrity controls by taking the following steps:

  • Enable and appropriately review audit trails for relevant GxP systems.
  • Eliminate shared accounts and establish individual user access.
  • Implement role-based access controls and periodic permission reviews.
  • Protect original records and maintain appropriate data backups.
  • Establish procedures for reviewing, investigating, and documenting data discrepancies.
  • Train employees on data integrity principles, including ALCOA+ concepts where applicable.

Organizations should also review computerized system controls to confirm that records remain complete, consistent, and traceable.

2. Incomplete Documentation and Record-Keeping Practices

Documentation provides evidence that pharmaceutical activities are performed according to approved procedures. Incomplete or inaccurate records can make it difficult to demonstrate that manufacturing, testing, and quality decisions were properly controlled.

Common documentation gaps include missing signatures, incomplete batch manufacturing records, undocumented changes, inconsistent entries, and delayed record completion.

In some cases, procedures may exist but employees may not follow them consistently. This creates a difference between documented requirements and actual operational practices.

How to Improve GMP Documentation

Organizations can improve documentation practices by:

  • Reviewing standard operating procedures (SOPs) regularly.
  • Ensuring batch records are completed accurately and at the time activities occur.
  • Verifying that required signatures, dates, and approvals are present.
  • Establishing controlled procedures for correcting records.
  • Conducting routine documentation reviews and internal audits.
  • Training employees on good documentation practices.

Documentation reviews should focus on both record completeness and the accuracy of the information recorded. Effective oversight can help identify recurring issues and prevent similar mistakes.

3. Weak Deviation Investigations and Ineffective CAPA

Deviations occur when an activity, process, result, or condition does not meet an approved requirement. Pharmaceutical companies must investigate significant deviations appropriately, assess potential product-quality impacts, and implement suitable corrective and preventive actions.

A common compliance weakness is an investigation that identifies the immediate problem without determining its underlying cause. For example, repeatedly retraining an employee may not resolve a recurring issue caused by unclear procedures, poor system design, or inadequate process controls.

CAPA effectiveness is equally important. Closing an action does not automatically demonstrate that the original problem has been resolved.

How to Strengthen Deviation Management

Organizations should:

  • Establish clear procedures for reporting and investigating deviations.
  • Use suitable root cause analysis methods.
  • Assess the potential impact on product quality and patient safety.
  • Identify corrective actions that address the actual cause.
  • Assign action owners and realistic completion dates.
  • Perform documented CAPA effectiveness checks.
  • Review deviation trends to identify recurring problems.

GMP quality system audits can help determine whether investigations are thorough, actions are appropriate, and recurring deviations are being managed effectively.

4. Inadequate Supplier Qualification and Oversight

Pharmaceutical manufacturers depend on suppliers for raw materials, packaging components, equipment, and outsourced services. Weak supplier controls can introduce quality risks into manufacturing and distribution processes.

Potential gaps include incomplete supplier qualification, insufficient risk assessments, outdated quality agreements, missing audit evidence, and inadequate monitoring of supplier performance.

Supplier approval should not be treated as a one-time activity. The level of oversight should reflect the supplier’s role, the criticality of supplied materials or services, and the risks associated with the supply chain.

How to Improve Supplier Management

Pharmaceutical organizations should:

  • Evaluate suppliers before approving them for use.
  • Conduct risk-based supplier assessments and audits.
  • Maintain current supplier qualification records.
  • Establish and periodically review relevant quality agreements.
  • Monitor supplier performance, complaints, deviations, and quality trends.
  • Reassess suppliers when significant changes or recurring issues occur.

GMP supplier audits can help identify weaknesses in supplier quality systems and determine whether existing controls are appropriate for the risks involved.

5. Inadequate Employee Training and Competency Assessment

Employees must understand the GMP requirements relevant to their responsibilities. Training gaps can lead to procedural errors, documentation problems, incorrect handling practices, and inconsistent execution of manufacturing or laboratory activities.

Common issues include outdated training records, incomplete onboarding, training assigned without appropriate completion evidence, and limited assessment of employee competency.

Simply recording attendance does not always demonstrate that employees understand or can correctly apply a procedure.

How to Address Training Gaps

Organizations should:

  • Maintain current GMP training matrices.
  • Provide role-specific training before employees perform relevant tasks independently.
  • Update training when procedures or responsibilities change.
  • Document training completion and competency assessments.
  • Evaluate training effectiveness through suitable assessments or observation.
  • Review recurring errors to identify additional training needs.

Regular training audits can help verify whether employees receive appropriate instruction and whether training records accurately reflect their qualifications and responsibilities.

6. Weak Change Control and Quality Risk Management

Changes to equipment, facilities, computerized systems, materials, suppliers, and manufacturing processes may affect product quality or regulatory compliance.

Weak change control can occur when changes are implemented without adequate assessment, approval, documentation, or verification. Organizations may also overlook the need for updated procedures, employee training, validation, or qualification activities.

How to Strengthen Change Control

Companies should evaluate proposed changes before implementation and document their potential impact on quality, validated states, regulatory commitments, and associated procedures.

A robust change control process should include:

  • Documented change requests and justification.
  • Appropriate quality risk assessments.
  • Review and approval by relevant departments.
  • Identification of validation, qualification, or training requirements.
  • Defined implementation responsibilities.
  • Verification that required actions are complete.
  • Post-implementation review where appropriate.

GMP compliance audits can assess whether change control procedures are followed consistently and whether implemented changes remain adequately controlled.

7. Inadequate Equipment Maintenance and Qualification

Pharmaceutical manufacturing and testing depend on equipment that performs reliably and remains suitable for its intended use. Inadequate maintenance, incomplete qualification records, overdue calibration, or unresolved equipment issues can create quality risks.

These problems may also affect the reliability of manufacturing parameters, laboratory results, and process performance.

How to Reduce Equipment-Related Compliance Risks

Organizations should maintain approved maintenance schedules, calibration programs, equipment logs, and qualification records. They should also document equipment failures and evaluate their potential impact on products or previously generated data.

Where applicable, companies should verify that equipment qualification and maintenance activities are completed according to approved procedures. GMP facility audits and GMP manufacturing audits can help evaluate whether equipment controls are appropriate and consistently implemented.

8. Poor Audit Trail Review and Computerized System Controls

Electronic systems support laboratory testing, manufacturing, inventory management, quality control, and batch release activities. However, inadequate system controls can make it difficult to identify unauthorized changes or reconstruct important events.

Common weaknesses include excessive user privileges, inadequate audit trail review procedures, incomplete system access reviews, and insufficient documentation of system-related incidents.

How to Improve Computerized System Oversight

Companies should define responsibilities for system administration, establish suitable access controls, and review audit trails according to documented procedures and risk. They should also maintain appropriate system documentation, investigate relevant anomalies, and ensure that changes are controlled.

Periodic reviews should confirm that computerized systems remain suitable for their intended use and that relevant records are appropriately protected.

9. Inadequate Internal Audits and Quality Oversight

Internal audits help organizations evaluate whether procedures and quality controls are working as intended. However, an internal audit program may be ineffective if it repeatedly reviews low-risk areas while overlooking critical operations or recurring quality problems.

Another weakness occurs when audit findings are documented but corrective actions are not completed or verified effectively.

How to Improve Internal Audit Programs

Organizations should establish risk-based audit schedules, define audit scope and criteria, use qualified auditors, and document objective evidence.

Audit findings should be assessed according to their significance, assigned to responsible owners, and tracked through appropriate corrective actions. Follow-up reviews should determine whether the actions have resolved the identified issues.

GMP quality system audits can provide an independent assessment of the effectiveness of internal audit processes and broader quality oversight.

10. Weak Regulatory Readiness and GMP Gap Assessment

Pharmaceutical companies should not wait for a scheduled regulatory inspection to identify compliance weaknesses. A lack of inspection preparation can lead to delayed document retrieval, inconsistent responses, unclear responsibilities, and unresolved quality issues.

A GMP gap assessment compares current practices with applicable regulatory requirements, approved procedures, and internal quality standards.

How to Conduct an Effective GMP Gap Assessment

An effective assessment should:

  1. Define the applicable regulatory and quality requirements.
  2. Review relevant procedures, records, and quality system documents.
  3. Evaluate manufacturing, laboratory, facility, and supplier controls as applicable.
  4. Identify and document compliance gaps using objective evidence.
  5. Assess the significance and potential impact of each gap.
  6. Develop a prioritized remediation plan with clear responsibilities.
  7. Track corrective actions and verify their effectiveness.

The assessment should be tailored to the organization’s activities and risk profile rather than relying on a generic checklist alone.

How GxP Cellators Helps Address GMP Compliance Gaps

GxP Cellators supports pharmaceutical and other regulated organizations through GMP auditing services designed to identify compliance weaknesses and support quality improvement.

A structured audit can help organizations evaluate existing controls, review relevant documentation, and identify areas requiring further investigation or corrective action.

GMP Compliance Audit Services

Depending on the organization’s requirements and agreed audit scope, support may include:

  • GMP Compliance Audits.
  • Pharmaceutical GMP Audits.
  • cGMP Compliance Audits.
  • GMP Quality System Audits.
  • GMP Supplier Audits.
  • GMP Facility Audits.
  • GMP Manufacturing Audits.
  • GMP Regulatory Compliance Audits.
  • GMP Gap Assessment Audits.
  • Data integrity, documentation, deviation, and CAPA reviews.

These services can help organizations assess whether their quality systems are appropriately designed, consistently implemented, and supported by adequate records.

Why Choose GxP Cellators?

Organizations evaluating GMP auditing support should consider auditor experience, knowledge of applicable regulations, independence, and the practical value of audit recommendations.

GxP Cellators focuses on identifying compliance gaps and providing actionable findings that organizations can use to plan improvements. Audit scope and applicable regulatory coverage should be agreed upon according to the facility’s operations, products, and requirements.

For GMP auditing support, visit the GxP Cellators contact page to discuss your organization’s needs.

Conclusion

GMP compliance gaps can affect product quality, data reliability, and regulatory readiness. Data integrity, documentation, deviation investigations, supplier oversight, employee training, change control, equipment management, computerized systems, internal audits, and inspection preparation all deserve appropriate attention.

In 2026, pharmaceutical organizations should take a proactive, risk-based approach to identifying and correcting these weaknesses. Regular GMP compliance audits and gap assessments can help reveal problems, prioritize improvements, and strengthen quality management systems.

GxP Cellators provides GMP auditing services to help organizations evaluate their compliance practices and identify opportunities for improvement. Contact the team to discuss your GMP audit requirements and develop an approach suited to your operations.

Frequently Asked Questions

1. What are the top GMP compliance gaps in 2026?

Common areas of concern include data integrity, documentation practices, deviation investigations, supplier qualification, employee training, change control, equipment management, and ineffective internal audits. The specific findings depend on the facility and applicable regulatory requirements.

2. Why is data integrity important in GMP compliance?

Data integrity helps ensure that records used to make pharmaceutical quality decisions are accurate, complete, consistent, and traceable. Weak data controls can undermine confidence in laboratory results, manufacturing records, and batch release decisions.

3. How can pharmaceutical companies improve deviation investigations?

Companies can improve investigations through effective root cause analysis, documented product-impact assessments, appropriate CAPA, clear ownership, and effectiveness checks. Reviewing trends can also help identify recurring issues.

4. What is the difference between a GMP audit and a GMP gap assessment?

A GMP audit systematically evaluates activities and controls against defined requirements. A GMP gap assessment focuses on identifying differences between current practices and applicable requirements. Both can support compliance improvement and inspection readiness.

5. How often should GMP compliance audits be conducted?

Audit frequency should depend on regulatory requirements, organizational procedures, risk assessments, previous findings, and changes to operations. Higher-risk activities may require more frequent reviews than lower-risk areas.

6. How do GMP supplier audits improve compliance?

Supplier audits evaluate whether suppliers have appropriate quality systems and controls. They can help identify weaknesses in qualification, documentation, material handling, and quality oversight, supporting better risk management.

7. How can GxP Cellators help identify GMP compliance gaps?

GxP Cellators offers GMP auditing services that can assess quality systems, documentation, supplier controls, manufacturing practices, and other agreed audit areas. Contact the team to discuss the scope required for your organization.

Contact GxP Cellators

If your organization needs support identifying GMP compliance gaps, evaluating quality systems, or preparing a risk-based audit plan, contact GxP Cellators.

Contact Page: https://www.gxpcellators.com/contact/

14/10/2026
GMP-Compliance-Audit-1-1280x720.webp

Introduction

Preparing for a GMP compliance audit requires careful planning, accurate documentation, trained personnel, and effective quality management systems. For pharmaceutical manufacturers and other regulated organizations, audit preparation is essential for identifying compliance gaps and maintaining product quality.

Good Manufacturing Practices (GMP) establish quality standards for the manufacturing, testing, handling, and distribution of regulated products. A GMP compliance audit evaluates whether an organization’s processes, facilities, documentation, and quality systems meet applicable regulatory requirements.

In 2026, organizations should pay particular attention to documentation accuracy, data integrity, corrective and preventive actions (CAPA), employee training, and risk management. Preparing in advance helps companies identify weaknesses and address them before an external audit or regulatory inspection.

This guide explains how to prepare for a GMP compliance audit, which documents to review, how to prepare employees, and how GxP Cellators can support your GMP audit readiness.

What Is a GMP Compliance Audit?

A GMP compliance audit is a systematic review of an organization’s quality systems, manufacturing activities, documentation, and procedures against applicable Good Manufacturing Practices requirements.

Depending on the organization, the audit may focus on production, laboratory operations, equipment maintenance, supplier qualification, warehouse activities, or quality management systems.

GMP audits may be conducted internally, by external auditors, by customers, or as part of supplier qualification. Regulatory inspections are conducted by the relevant authorities under their applicable regulatory frameworks.

The primary objective is to identify compliance gaps, evaluate potential risks, and confirm that suitable controls are in place to protect product quality and patient safety.

Why Is GMP Audit Preparation Important?

Effective GMP audit preparation helps organizations identify weaknesses before they become significant compliance issues. It also allows teams to organize evidence, review procedures, and confirm that established controls are working as intended.

The main benefits include:

  • Improved compliance: Identify gaps against applicable GMP requirements and internal procedures.
  • Better documentation: Ensure records are complete, accurate, traceable, and readily available.
  • Stronger data integrity: Review how regulated data is created, recorded, checked, and maintained.
  • Reduced operational risks: Identify weaknesses in manufacturing, testing, equipment, and facility controls.
  • Improved employee readiness: Help personnel understand their responsibilities and applicable procedures.
  • Effective corrective actions: Resolve identified issues through documented investigations and CAPA plans.

Although preparation cannot guarantee a successful audit, it can help organizations demonstrate control over their processes and respond to audit findings more effectively.

Step 1: Conduct a GMP Gap Assessment

Start by reviewing your current quality management system against the GMP requirements applicable to your products, activities, and markets.

A gap assessment helps determine whether existing procedures, records, and operational controls meet established requirements. It also provides a clear starting point for your audit preparation plan.

During the assessment, review the following areas:

  • Quality management systems and responsibilities
  • Standard operating procedures (SOPs)
  • Manufacturing and laboratory documentation
  • Equipment qualification and calibration
  • Employee training and competency records
  • Deviation management and CAPA
  • Change control procedures
  • Supplier qualification and monitoring
  • Facility maintenance and cleaning
  • Data integrity and record management

Once gaps have been identified, classify them according to their potential impact on product quality, patient safety, data reliability, and regulatory compliance.

Next, assign responsibilities, establish realistic deadlines, and track corrective actions until completion. High-risk issues should receive appropriate priority based on their potential impact.

Step 2: Review and Update GMP Documentation

Documentation is a major part of GMP audit preparation. Auditors may review procedures, records, and supporting evidence to determine whether activities were performed according to approved requirements.

Before an audit, verify that documents are current, approved, controlled, and available to authorized personnel.

Essential Documents to Review

1. Quality Manual and SOPs

Review the quality manual, standard operating procedures, work instructions, and related controlled documents. Confirm that they reflect current practices and applicable requirements.

2. Batch Manufacturing Records

Check batch production and packaging records for completeness, consistency, required approvals, and traceability. Investigate missing entries or unexplained discrepancies.

3. Laboratory and Analytical Records

Review testing records, analytical results, instrument records, and investigations involving unexpected results. Ensure that records are complete and scientifically justified.

4. Deviation and CAPA Records

Confirm that deviations have been investigated appropriately. CAPA records should explain the root cause, corrective action, preventive action where applicable, assigned responsibilities, and effectiveness checks.

5. Change Control Records

Review changes involving equipment, processes, materials, software, facilities, and procedures. Confirm that changes were assessed, approved, implemented, and verified according to established procedures.

6. Training Records

Verify that employees have completed required training before performing assigned activities. Records should show the training completed and any applicable competency assessments.

7. Equipment and Maintenance Records

Review calibration certificates, preventive maintenance schedules, equipment qualification documents, and records of relevant repairs or failures.

Keep documents organized so that the responsible team can retrieve the requested records without unnecessary delays.

Step 3: Prepare Your Facility and Equipment

A GMP compliance audit may include a physical walkthrough of manufacturing areas, laboratories, warehouses, and other controlled environments.

Before the audit, confirm that facilities are maintained in accordance with applicable GMP requirements and approved procedures.

Key Facility Preparation Activities

  • Ensure manufacturing and laboratory areas are clean and appropriately maintained.
  • Verify that equipment calibration and preventive maintenance are up to date.
  • Review cleaning and sanitation procedures and their supporting records.
  • Check pest control arrangements and associated documentation.
  • Confirm that materials are appropriately identified and stored.
  • Review environmental monitoring records where applicable.
  • Verify that equipment status labels and maintenance records are accurate.
  • Check that deviations involving facilities or equipment have been documented and addressed.

For organizations operating cleanrooms, the review may also include environmental controls, pressure differentials, contamination prevention, and relevant qualification records.

The exact checks depend on the facility, product type, manufacturing process, and applicable regulatory requirements.

Step 4: Prepare Employees for the Audit

Employees play an important role in demonstrating GMP compliance. Even when documentation is complete, unclear responsibilities or unfamiliarity with procedures can create avoidable problems during an audit.

Prepare employees by reviewing their training status and explaining how the audit will be conducted.

How to Improve Employee Audit Readiness

Review GMP responsibilities: Ensure that employees understand the procedures relevant to their roles.

Verify training completion: Check that required GMP and job-specific training is documented and current.

Conduct awareness sessions: Explain the audit process, expected professional behaviour, and how employees should respond to questions.

Practice procedure-based questions: Ask employees to explain their routine activities and identify the applicable SOPs.

Clarify escalation procedures: Employees should understand how to report deviations, errors, unexpected events, and potential quality issues.

Employees should answer questions honestly and clearly. They should not guess when they do not know an answer. Instead, they should follow the organization’s established process for obtaining accurate information.

Step 5: Conduct a Mock GMP Audit

A mock GMP audit simulates an actual audit to identify weaknesses before the scheduled assessment. It helps organizations evaluate documentation, facility conditions, employee readiness, and the effectiveness of existing quality controls.

An effective mock audit should follow a structured audit plan based on the organization’s operations and applicable GMP requirements.

What Should a Mock Audit Include?

  • Review of quality management system documentation
  • Sampling of batch and laboratory records
  • Assessment of deviation and CAPA management
  • Interviews with relevant personnel
  • Facility and equipment walkthroughs
  • Review of supplier qualification records
  • Evaluation of data integrity controls
  • Verification of previous audit findings and corrective actions

After the mock audit, document the observations and supporting evidence. Classify findings according to the organization’s established risk criteria and applicable procedures.

Develop corrective action plans for identified gaps, assign responsibilities, and establish target completion dates. Where necessary, verify whether corrective actions have resolved the underlying issue.

A mock audit is most useful when it evaluates actual practices rather than simply checking whether documents exist.

Step 6: Review Data Integrity and Electronic Records

Data integrity is an important part of pharmaceutical quality and GMP compliance. Organizations should ensure that regulated data remains accurate, complete, consistent, and reliable throughout its lifecycle.

During preparation, review both paper-based and electronic records, depending on the systems used.

Consider the following questions:

  • Are records attributable to the individuals who performed the activities?
  • Are entries recorded at the appropriate time?
  • Are original records or appropriate verified copies maintained?
  • Are records accurate, complete, and consistent?
  • Are corrections documented with appropriate justification and traceability?
  • Are electronic systems access-controlled and appropriately managed?
  • Are audit trails reviewed where required?
  • Are backup, retention, and retrieval arrangements suitable for the relevant records?

The ALCOA+ principles can help organizations evaluate important data integrity characteristics, including attributable, legible, contemporaneous, original, accurate, complete, consistent, enduring, and available records.

Review the applicable procedures and regulatory expectations before the audit, particularly where computerized systems and electronic records are involved.

Step 7: Review Supplier Qualification and Quality Controls

Suppliers can affect the quality, safety, and reliability of pharmaceutical products. Therefore, supplier qualification and monitoring may form an important part of GMP audit preparation.

Review whether suppliers have been evaluated and approved according to established procedures. Check that supplier risks are assessed and that relevant quality agreements, certificates, specifications, and supporting records are available.

Your review may include:

  • Approved supplier lists
  • Supplier qualification and evaluation records
  • Supplier audit reports
  • Material specifications and certificates of analysis
  • Quality agreements, where applicable
  • Supplier-related deviations and complaints
  • Corrective actions and follow-up assessments

Risk-based supplier oversight helps organizations focus resources on suppliers and materials that could have a greater impact on product quality or regulatory compliance.

Step 8: Develop a CAPA Plan and Verify Corrective Actions

Identifying gaps is only one part of GMP audit preparation. Organizations must also determine how identified issues will be corrected and how recurrence will be prevented.

A CAPA plan should clearly document the problem, investigation, root cause where established, proposed actions, responsible personnel, and target completion dates.

For effective CAPA management:

  1. Describe the issue clearly and objectively.
  2. Investigate the root cause using an appropriate method.
  3. Determine suitable corrective and preventive actions.
  4. Assign responsibilities and realistic deadlines.
  5. Document implementation and supporting evidence.
  6. Evaluate effectiveness where required by the applicable procedure.
  7. Escalate overdue or ineffective actions appropriately.

Avoid closing actions only because a task has been completed. The organization should also consider whether the underlying cause has been addressed and whether further action is necessary.

Common Mistakes to Avoid During GMP Audit Preparation

Even well-established organizations can experience difficulties when audit preparation is rushed or poorly coordinated.

Common mistakes include:

  • Updating documents without reviewing actual work practices.
  • Leaving deviations or CAPA actions unresolved without appropriate justification.
  • Providing incomplete or inconsistent records.
  • Overlooking employee training requirements.
  • Ignoring supplier qualification and monitoring gaps.
  • Failing to investigate recurring quality issues.
  • Conducting mock audits without documented follow-up.
  • Making unsupported claims about compliance.
  • Failing to verify whether corrective actions are effective.

A structured preparation plan helps organizations address these issues systematically rather than relying on last-minute document collection.

How GxP Cellators Helps You Prepare for a GMP Compliance Audit

GxP Cellators supports regulated organizations through GxP consulting, auditing, and quality-related services. Its GMP audit preparation support can help organizations evaluate their current processes, identify potential gaps, and improve audit readiness.

Depending on the scope and agreed requirements, support may include:

  • Pre-audit GMP gap assessments
  • Quality system and documentation reviews
  • Mock GMP audits
  • Review of deviations and CAPA processes
  • GMP training and employee awareness support
  • Supplier and quality-system audit support
  • Risk-based audit preparation
  • Inspection readiness recommendations

GxP Cellators can help organizations focus on practical improvements and prioritize issues according to their potential compliance impact.

Its approach can be tailored to the organization’s operations, quality systems, and applicable regulatory framework. The specific scope of services should be confirmed before engagement.

To discuss your requirements, visit the GxP Cellators Contact Page.

Why Choose GxP Cellators for GMP Audit Preparation?

Choosing the right audit support partner can help your team prepare more systematically and identify areas that require further attention.

GxP Cellators focuses on practical compliance support for regulated organizations. When evaluating audit preparation support, organizations should consider:

  • Relevant pharmaceutical and quality-system experience
  • Familiarity with applicable regulatory expectations
  • A risk-based approach to identifying gaps
  • Clear and actionable recommendations
  • Appropriate confidentiality arrangements
  • Documented findings and follow-up recommendations

GMP audit preparation should reflect the organization’s actual processes rather than rely on a generic checklist alone. A tailored approach helps teams focus on the areas most relevant to their products, facilities, and compliance obligations.

Frequently Asked Questions

1. How far in advance should I prepare for a GMP compliance audit?

Preparation should ideally begin several months before a scheduled audit. Three to six months can be a useful planning period for complex operations, although the required time depends on the organization’s size, audit scope, identified gaps, and corrective action workload.

2. What documents should I prepare for a GMP compliance audit?

Important documents may include the quality manual, SOPs, batch records, laboratory records, deviation reports, CAPA records, change control documents, training records, equipment maintenance records, and supplier qualification files. The exact list depends on the audit scope.

3. How can I prepare employees for a GMP compliance audit?

Review employee training records, explain relevant GMP responsibilities, and conduct awareness sessions or mock interviews. Employees should understand their procedures, answer questions honestly, and follow established processes when they need clarification.

4. What is a mock GMP audit?

A mock GMP audit is a planned assessment that simulates aspects of an actual audit. It helps identify documentation gaps, process weaknesses, and training needs so that the organization can take appropriate corrective action before the scheduled audit.

5. What are the most common GMP audit findings?

Potential findings include incomplete documentation, inadequate deviation investigations, ineffective CAPA, insufficient training records, equipment maintenance gaps, data integrity weaknesses, and inadequate supplier controls. Actual findings depend on the facility, operations, and applicable requirements.

6. What is the difference between a GMP audit and a regulatory inspection?

A GMP audit may be conducted internally or by an external organization to evaluate compliance with applicable requirements and internal standards. A regulatory inspection is conducted by a regulatory authority under its legal mandate. Their scope, purpose, and outcomes may differ.

7. How does GxP Cellators support GMP audit preparation?

GxP Cellators provides GxP consulting and auditing support that may include gap assessments, documentation reviews, mock audits, CAPA-related support, and inspection readiness recommendations, depending on the agreed project scope.

8. How can I contact GxP Cellators for GMP audit preparation support?

Visit the GxP Cellators Contact Page to discuss your organization’s audit preparation requirements and determine which services may be suitable.

Conclusion

Preparing for a GMP compliance audit involves more than collecting documents before an auditor arrives. Organizations need to review their quality systems, maintain reliable records, prepare employees, assess facility conditions, and address identified compliance gaps.

A practical preparation plan should include a risk-based gap assessment, documentation review, facility checks, employee training, a mock audit, and appropriate CAPA follow-up. In addition, reviewing data integrity and supplier controls can help organizations identify important areas that may require attention.

With a structured approach, organizations can improve their understanding of GMP requirements and prepare more effectively for audits and regulatory inspections.

GxP Cellators offers GxP consulting and auditing support to help organizations evaluate their compliance needs and identify practical improvement opportunities.

Need help preparing for aGMP compliance audit? Visit GxP Cellators to discuss your audit preparation requirements.


14/10/2026
GMP-Compliance-Audit-1280x720.webp

Introduction

Good Manufacturing Practice (GMP) compliance is essential for pharmaceutical companies that manufacture, test, package, and distribute medicines. It helps ensure that products meet established quality standards and remain safe, effective, and consistent. A well-planned GMP compliance audit also helps companies identify weaknesses before they become serious quality or regulatory concerns.

In 2026, pharmaceutical organizations must pay close attention to documentation, data integrity, quality management systems, supplier oversight, equipment qualification, and manufacturing controls. An effective audit reviews these areas systematically and checks whether documented procedures are followed in daily operations.

A GMP compliance audit checklist provides a structured way to evaluate these requirements. It helps quality teams review their systems, identify gaps, document findings, and establish corrective and preventive actions (CAPA).

GxP Cellators supports pharmaceutical organizations with GMP auditing services, quality system assessments, supplier audits, facility audits, and regulatory compliance support. This guide explains the main areas companies should review when preparing for a GMP compliance audit in 2026.

What Is a GMP Compliance Audit?

A GMP compliance audit is a systematic review of pharmaceutical processes, facilities, records, equipment, and quality systems. Its purpose is to determine whether operations follow applicable GMP requirements, approved procedures, and internal quality standards.

Depending on the audit’s objective, the review may cover an entire manufacturing facility or focus on a particular area, such as laboratory operations, supplier qualification, data integrity, or production controls.

GMP audits may be conducted internally, by qualified external auditors, or as part of supplier qualification and oversight. They are different from regulatory inspections, although audit findings can help organizations improve their readiness for inspections by authorities such as the US Food and Drug Administration (FDA).

GMP Compliance Audit Checklist: 8 Essential Areas

The following checklist can help pharmaceutical companies organize their internal reviews and identify areas that need further investigation. The specific requirements should be adapted to the applicable regulations, product type, facility, and market.

1. Quality Management System (QMS)

The quality management system provides the foundation for GMP compliance. Auditors should evaluate whether the system is documented, implemented, maintained, and reviewed regularly.

Checklist:

  • Is the quality management system documented and approved?
  • Is the quality manual current and consistent with actual practices?
  • Are quality objectives defined, monitored, and reviewed?
  • Are management reviews conducted and documented at appropriate intervals?
  • Are quality metrics tracked to identify recurring issues and trends?
  • Are deviations, complaints, investigations, and CAPA managed through approved procedures?

An effective QMS should demonstrate that quality issues are investigated appropriately and that corrective actions address their underlying causes. Auditors should also check whether completed CAPAs are verified for effectiveness.

2. Personnel and GMP Training

Employees must understand the procedures and responsibilities associated with their roles. Inadequate training can lead to documentation errors, incorrect manufacturing practices, and avoidable compliance gaps.

Checklist:

  • Are job descriptions current and approved?
  • Are employees trained before performing assigned tasks independently?
  • Are training records complete, accurate, and readily available?
  • Is GMP training conducted at appropriate intervals?
  • Are employees qualified for their assigned responsibilities?
  • Is additional training provided when procedures or responsibilities change?

Auditors should verify training effectiveness rather than relying only on attendance records. For example, personnel may need to demonstrate that they understand critical procedures before performing activities that affect product quality.

3. Facilities, Equipment, and Utilities

Pharmaceutical facilities must be designed, maintained, and operated to reduce contamination risks and support consistent product quality. Equipment and utilities must also remain suitable for their intended use.

Checklist:

  • Are manufacturing and storage areas maintained in a clean and suitable condition?
  • Are equipment qualification and calibration records available?
  • Is preventive maintenance performed according to approved schedules?
  • Are cleaning procedures documented and followed?
  • Are pest control activities documented and monitored?
  • Are critical utilities qualified and monitored where required?
  • Are environmental conditions controlled according to product and process requirements?

For facilities with controlled environments, auditors should review applicable environmental monitoring, cleaning controls, and contamination prevention measures. Any deficiencies should be assessed for their potential impact on product quality and patient safety.

4. Documentation and Record Management

Accurate documentation is a central GMP requirement. Records should provide reliable evidence that manufacturing, testing, and quality activities were performed according to approved procedures.

Checklist:

  • Are batch manufacturing and packaging records complete?
  • Are entries recorded at the time activities are performed?
  • Are corrections traceable and appropriately justified?
  • Are deviations documented and investigated?
  • Is change control reviewed and approved before implementation, where required?
  • Are records retained for the applicable retention period?
  • Are electronic and paper records protected against unauthorized changes?

Auditors should also examine whether actual practices match written procedures. A procedure may appear compliant on paper, but differences in day-to-day execution can create significant quality risks.

5. Production and Process Controls

Manufacturing processes must operate under controlled conditions to produce consistent products. Auditors should assess whether critical process parameters, instructions, and in-process checks are properly established and followed.

Checklist:

  • Are manufacturing processes validated or otherwise appropriately qualified where required?
  • Are approved manufacturing instructions available to personnel?
  • Are in-process controls established and documented?
  • Are batch records reviewed before batch release?
  • Are material quantities, yields, and reconciliations checked?
  • Are out-of-specification (OOS) results investigated?
  • Are deviations from approved processes documented and assessed?

The audit should establish whether process controls are effective and whether unusual results are investigated thoroughly. Repeated deviations or unexplained variations may indicate weaknesses that require a deeper review.

6. Quality Control and Laboratory Operations

Quality control activities help confirm that raw materials, in-process samples, and finished products meet established specifications. Laboratory controls are therefore an important part of a GMP compliance audit.

Checklist:

  • Are specifications approved for raw materials and finished products?
  • Are analytical methods validated or verified, as applicable?
  • Are laboratory instruments calibrated and maintained?
  • Is stability testing conducted according to approved protocols?
  • Are laboratory records complete and traceable?
  • Are OOS and out-of-trend results investigated appropriately?
  • Are reference standards and laboratory reagents controlled as required?

Auditors should examine the investigation process for unexpected laboratory results. Repeating a test without a scientifically justified investigation may fail to address the original problem.

7. Supplier and Vendor Management

Suppliers can directly affect pharmaceutical product quality. Companies should therefore establish appropriate controls for qualifying, monitoring, and periodically reviewing suppliers according to risk.

Checklist:

  • Are suppliers evaluated and approved before use?
  • Are supplier qualification records maintained?
  • Are quality agreements established where appropriate?
  • Are supplier audits conducted according to documented risk criteria?
  • Is supplier performance monitored using relevant quality indicators?
  • Are supplier-related deviations and complaints investigated?
  • Are changes to critical suppliers or materials assessed and approved?

Risk-based supplier oversight helps companies focus their resources on suppliers that may have the greatest impact on product quality. GMP supplier audits can also identify gaps in documentation, manufacturing controls, and quality management before they affect the receiving organization.

8. Data Integrity and Electronic Records

Data integrity remains a critical part of pharmaceutical quality oversight. Records must be reliable, complete, consistent, and protected throughout their lifecycle.

Checklist:

  • Are audit trails enabled and reviewed where applicable?
  • Are system access permissions appropriate for each user’s responsibilities?
  • Are electronic signatures controlled and attributable to individual users?
  • Are records protected against unauthorized alteration or deletion?
  • Are backup and recovery procedures established and tested?
  • Are computerized systems validated or otherwise appropriately controlled for their intended use?
  • Do records follow ALCOA+ principles where applicable?

ALCOA+ means that data should be attributable, legible, contemporaneous, original, and accurate, along with being complete, consistent, enduring, and available.

A strong data integrity review examines system configuration, user access, audit trail review, record handling, and actual working practices. It should also determine whether identified issues could affect product quality or the reliability of decisions made using the data.

How to Conduct a GMP Compliance Audit

A structured audit process helps ensure that findings are supported by evidence and that identified problems lead to meaningful improvements.

Step 1: Define the Audit Scope

Identify the facility, department, process, product, or quality system to be reviewed. Determine the applicable GMP requirements and establish clear audit objectives.

Step 2: Review Documents Before the Audit

Examine relevant SOPs, training records, batch documentation, validation reports, deviation records, CAPA documentation, and previous audit findings. This preparation helps auditors identify potential risk areas.

Step 3: Conduct Interviews and On-Site Reviews

Speak with relevant personnel, observe actual operations, and compare working practices with approved procedures. Review objective evidence rather than relying only on verbal explanations.

Step 4: Document Findings and Assess Risk

Record each finding clearly, including the evidence, applicable requirement, and potential quality impact. Prioritize findings according to their severity and risk rather than treating every observation equally.

Step 5: Establish CAPA and Verify Effectiveness

Assign responsibilities and realistic completion dates for corrective actions. Investigate root causes and verify whether implemented actions prevent recurrence. Closure should be based on documented evidence and effectiveness checks, not simply completion of assigned tasks.

How GxP Cellators Supports GMP Compliance Audits

GxP Cellators provides GMP auditing and compliance support to help pharmaceutical organizations evaluate their quality systems, identify weaknesses, and strengthen audit readiness.

Depending on the organization’s requirements and agreed scope, support may include:

  • Full-scope GMP compliance audits.
  • Pre-inspection readiness assessments.
  • Mock regulatory inspections.
  • GMP quality system audits.
  • Data integrity audits.
  • GMP supplier and vendor audits.
  • GMP facility and manufacturing audits.
  • CAPA verification and follow-up support.
  • GMP gap assessments and remediation planning.

GxP Cellators can help organizations assess applicable FDA, EMA, Health Canada, MHRA, and WHO requirements relevant to their operations and target markets. The audit scope should be tailored to the organization’s products, processes, regulatory obligations, and identified risks.

Why Choose GxP Cellators?

A useful audit should do more than identify documentation errors. It should help an organization understand the underlying causes of compliance gaps and determine practical steps for addressing them.

GxP Cellators focuses on structured assessments, evidence-based findings, risk-based reviews, and actionable recommendations. These services can help quality teams prioritize remediation, improve oversight, and prepare more effectively for regulatory inspections.

To discuss your requirements, visit the GxP Cellators contact page.

Conclusion

A GMP compliance audit checklist helps pharmaceutical companies assess their quality management systems, personnel training, facilities, documentation, production processes, laboratory controls, supplier oversight, and data integrity. Reviewing these areas systematically can reveal weaknesses before they develop into more serious compliance concerns.

However, a checklist alone cannot guarantee GMP compliance. Organizations must also evaluate applicable requirements, maintain accurate records, investigate deviations, implement effective CAPA, and verify that corrective actions work as intended.

GxP Cellators provides GMP auditing services, quality system reviews, supplier audits, data integrity assessments, and gap assessment support to help pharmaceutical organizations strengthen their compliance programs.

If your organization needs assistance preparing for an audit or identifying potential compliance gaps, contact GxP Cellators to discuss an appropriate audit approach.

Frequently Asked Questions

1. What is a GMP compliance audit?

A GMP compliance audit is a systematic examination of pharmaceutical facilities, processes, records, and quality systems to assess compliance with applicable Good Manufacturing Practice requirements.

2. How often should GMP compliance audits be conducted?

Audit frequency should be based on applicable regulatory requirements, internal procedures, and risk. Many organizations establish annual audit schedules, while higher-risk processes, significant changes, or previous findings may justify more frequent reviews. Annual auditing is not a universal requirement for every process or situation.

3. What are the common findings in GMP compliance audits?

Common findings may involve incomplete documentation, inadequate training, equipment calibration issues, weak deviation investigations, ineffective CAPA, data integrity deficiencies, and insufficient supplier oversight. Actual findings depend on the facility and audit scope.

4. What should a GMP compliance audit checklist include?

A comprehensive checklist should cover the quality management system, personnel training, facilities and equipment, documentation, production controls, quality control, supplier management, and data integrity. Additional areas may be necessary depending on the product, process, and applicable regulations.

5. What is the difference between a GMP audit and a regulatory inspection?

A GMP audit is generally conducted by an organization or its appointed auditors to assess compliance and identify improvement opportunities. A regulatory inspection is conducted by a regulatory authority under its legal mandate. Internal and external audits can help improve inspection readiness, but they do not replace regulatory inspections.

6. How does GxP Cellators support GMP compliance audits?

GxP Cellators offers GMP compliance audits, pre-inspection readiness assessments, mock inspections, quality system audits, data integrity reviews, supplier audits, and CAPA follow-up support, depending on the agreed project scope.

7. How can I contact GxP Cellators for GMP audit support?

Visit the GxP Cellators contact page to discuss your organization’s audit requirements and potential compliance support.


14/10/2026
AI-data-integrity-risks-pharma-1280x720.webp

Introduction

Data integrity is essential for maintaining quality, safety, and regulatory compliance in the pharmaceutical industry. As pharmaceutical companies increasingly use artificial intelligence (AI) and machine learning (ML), protecting the accuracy, completeness, consistency, and traceability of data has become more important than ever.

AI systems depend on data to generate predictions, identify patterns, support quality decisions, and automate specific processes. However, poor-quality training data, incomplete records, unauthorized changes, and weak documentation can affect the reliability of AI-generated results.

These issues can create challenges for organizations operating under Good Manufacturing Practices (GMP), Good Laboratory Practices (GLP), and other GxP requirements.

AI data integrity risks in pharma require careful assessment because problems may not always be visible through routine system checks. A model can produce convincing results even when its underlying data is incomplete, biased, outdated, or incorrectly processed.

GxP audits help pharmaceutical organizations identify these weaknesses, review supporting evidence, and determine whether appropriate controls are in place. GxP Cellators supports organizations through specialized GxP auditing services, including reviews of AI-related data integrity risks.

What Are AI Data Integrity Risks in Pharma?

AI data integrity risks are problems that affect the accuracy, completeness, reliability, traceability, or security of data used by AI systems.

These risks can arise during data collection, model training, data processing, system operation, or model updates. They may also occur when organizations lack clear procedures for reviewing AI-generated outputs and documenting human decisions.

For example, an AI tool used to identify unusual manufacturing results may provide unreliable recommendations if it receives incomplete process data. Similarly, an AI application used in quality control may produce misleading results if its training data does not adequately represent real operating conditions.

In regulated environments, companies need appropriate documentation, access controls, audit trails, change management, and human oversight based on the system’s intended use and risk.

Five Major AI Data Integrity Risks and How GxP Audits Identify Them

1. Poor Training Data Quality

Training data quality is one of the most important factors affecting AI reliability. If a model is trained using inaccurate, incomplete, duplicated, or unrepresentative data, its outputs may be misleading.

In pharmaceutical operations, this could affect applications used for manufacturing analysis, laboratory investigations, quality monitoring, or predictive maintenance.

For example, an AI model trained using incomplete manufacturing records may fail to identify a recurring process deviation.

How GxP audits identify this risk:

  • Review training data sources and their suitability for the intended use.
  • Assess data completeness, accuracy, consistency, and representativeness.
  • Examine missing values, duplicate records, and data preprocessing activities.
  • Review documentation supporting data cleaning and transformation.
  • Verify that identified data quality issues are evaluated and addressed.

These checks help organizations understand whether the data supporting an AI application is appropriate for its intended purpose.

2. Missing Training Data Provenance and Traceability

Data provenance explains where data originated, how it was collected, and what changes occurred before it was used by an AI model.

Without sufficient provenance records, an organization may struggle to demonstrate that its training data came from appropriate sources or was processed using controlled procedures.

This becomes particularly important when data is collected from multiple systems, external providers, laboratory platforms, or manufacturing databases.

How GxP audits identify this risk:

  • Review records identifying original data sources.
  • Assess data lineage and traceability documentation.
  • Examine data transfer and transformation procedures.
  • Verify source qualification and approval where applicable.
  • Check whether relevant data versions can be identified and reconstructed.

A documented data trail helps organizations investigate unexpected outputs and explain how information was used to develop or operate an AI model.

3. Operational Data Integrity Issues

AI data integrity risks can continue after a model has been deployed. Operational problems may arise when data is transferred incorrectly, modified without authorization, lost during processing, or recorded without sufficient traceability.

For example, an AI system monitoring production equipment may receive incorrect sensor readings because of a data integration problem. As a result, the system could generate inaccurate alerts or recommendations.

How GxP audits identify this risk:

  • Review audit trails for relevant AI inputs, outputs, and changes.
  • Assess user access permissions and authorization controls.
  • Examine data backup and recovery procedures.
  • Review data transfer interfaces and integration controls.
  • Evaluate data integrity monitoring and incident management.
  • Check whether discrepancies are investigated and documented.

Auditors should also determine whether controls are appropriate for the system’s intended use and the potential impact of incorrect information on product quality or patient safety.

4. Inadequate Model Change Documentation

AI models and their supporting systems may change over time. Updates can affect training datasets, model parameters, algorithms, software components, interfaces, and intended functionality.

If these changes are not properly documented, organizations may find it difficult to determine which model version generated a particular result or whether an update affected system performance.

In regulated pharmaceutical environments, uncontrolled changes can create significant compliance and traceability concerns.

How GxP audits identify this risk:

  • Review model version histories and change records.
  • Assess change control procedures and approval requirements.
  • Examine the documented impact assessments for model updates.
  • Verify testing and validation evidence following significant changes.
  • Review criteria for determining when revalidation or additional testing is required.
  • Confirm that previous versions and relevant records remain traceable where necessary.

A risk-based change management process helps ensure that AI system modifications are evaluated, approved, tested, and documented before implementation, as appropriate.

5. Weak Human Oversight Documentation

AI systems may support important decisions, but organizations must establish appropriate oversight based on the system’s intended use and risk. Human review is especially important when AI outputs influence quality investigations, manufacturing decisions, laboratory assessments, or other GxP activities.

Problems can arise when employees accept AI recommendations without sufficient review or when decisions to override, reject, or escalate an output are not documented.

How GxP audits identify this risk:

  • Review procedures defining human responsibilities and review requirements.
  • Assess records of human interventions and decisions.
  • Examine training records for employees using AI applications.
  • Verify escalation procedures for unexpected or unreliable outputs.
  • Review evidence that critical AI-generated recommendations receive appropriate review.
  • Assess how disagreements between AI outputs and human assessments are handled.

Clear responsibilities and appropriate documentation help maintain accountability when AI tools support regulated activities.

How GxP Audits Help Identify AI Data Integrity Problems

A structured GxP audit examines more than the technical performance of an AI application. It also evaluates the controls, procedures, records, and responsibilities that support its use in a regulated environment.

Depending on the application and audit scope, the assessment may include the following activities.

Review of Data Governance

Auditors assess whether data ownership, access, retention, processing, and quality responsibilities are clearly defined. They also examine whether relevant procedures are documented and followed.

Assessment of Audit Trails and Access Controls

Audit trail reviews help determine whether relevant activities and changes are traceable. Access control assessments examine whether users have appropriate permissions and whether unauthorized changes are adequately restricted.

Review of Validation and Change Control

Auditors examine the evidence supporting the AI system’s intended use, including relevant testing, validation, change assessments, and ongoing monitoring. The depth of review should reflect the system’s risk and applicable regulatory requirements.

Evaluation of Deviations and CAPA

When data integrity issues are identified, auditors review how the organization investigates the problem, evaluates its impact, determines the root cause, and implements corrective and preventive actions (CAPA).

Follow-up activities can help determine whether corrective actions were implemented effectively and whether the underlying issue has been adequately addressed.

How GxP Cellators Supports AI Data Integrity Audits

GxP Cellators provides GxP auditing and compliance support for organizations working in regulated industries. For companies adopting AI in pharmaceutical operations, an appropriately scoped audit can help identify weaknesses in data governance, documentation, traceability, and control processes.

AI-related audit support may include:

  • Training data quality audits.
  • Training data provenance and traceability reviews.
  • Operational data integrity assessments.
  • Model change documentation reviews.
  • Human oversight documentation reviews.
  • Audit trail and access control reviews.
  • Mock AI audits and inspection readiness assessments.
  • CAPA verification and follow-up activities.

The scope of each engagement should reflect the organization’s AI application, intended use, relevant GxP processes, and applicable regulatory expectations.

Why Choose GxP Cellators?

Organizations need practical findings that help them understand their compliance risks and determine appropriate next steps.

GxP Cellators supports this process through:

  • GxP-focused expertise: Assessments aligned with the relevant quality and compliance environment.
  • Risk-based audit planning: Audit activities tailored to the intended use and potential impact of the AI application.
  • Regulatory awareness: Consideration of applicable FDA, EMA, Health Canada, MHRA, and WHO requirements and guidance.
  • Actionable findings: Clear observations that help organizations prioritize remediation.
  • Confidentiality: Appropriate protection of proprietary information and audit documentation.

The exact audit scope and applicable regulatory expectations should be confirmed for each engagement.

Best Practices for Managing AI Data Integrity Risks

Pharmaceutical organizations can strengthen AI data integrity by establishing clear controls throughout the system lifecycle.

  1. Define data quality requirements: Establish suitable criteria for data accuracy, completeness, consistency, and representativeness.
  2. Maintain data traceability: Document data sources, transformations, relevant versions, and processing activities.
  3. Apply access controls: Restrict system and data access according to assigned responsibilities.
  4. Maintain appropriate audit trails: Ensure relevant changes and activities can be reconstructed where required.
  5. Control model changes: Assess, approve, test, and document changes according to risk and established procedures.
  6. Provide employee training: Ensure personnel understand AI limitations, data integrity responsibilities, and escalation procedures.
  7. Review incidents and deviations: Investigate unexpected results and implement suitable corrective actions.
  8. Conduct periodic risk-based audits: Reassess controls when systems, data sources, intended uses, or regulatory expectations change.

These practices can help organizations improve oversight and identify weaknesses before they lead to more significant compliance problems.

Frequently Asked Questions

What are the main AI data integrity risks in pharma?

The main risks include poor training data quality, missing data provenance, operational data integrity problems, inadequate model change documentation, and weak human oversight. These issues can affect AI reliability, traceability, and GxP compliance.

How can GxP audits identify AI data integrity risks?

GxP audits can identify these risks by reviewing training data sources, data lineage, audit trails, access controls, model change records, validation evidence, and human oversight procedures. Auditors can also evaluate deviation investigations and CAPA effectiveness.

Why is training data quality important for pharmaceutical AI systems?

Training data quality affects how reliably an AI model identifies patterns and generates outputs. Inaccurate, incomplete, or unrepresentative data can lead to unreliable recommendations and may affect decisions involving pharmaceutical quality or regulated processes.

What is data provenance in AI auditing?

Data provenance documents where data originated, how it was processed, and how it changed before being used by an AI system. It supports traceability and helps organizations investigate unexpected outputs or demonstrate appropriate data governance.

How does GxP Cellators support AI data integrity audits?

GxP Cellators offers GxP auditing and compliance support that may include training data quality reviews, provenance assessments, operational data integrity audits, model change documentation reviews, audit trail assessments, and CAPA follow-up, depending on the agreed scope.

How can I contact GxP Cellators for AI data integrity audit support?

Visit the GxP Cellators to discuss your organization’s AI data integrity risks, audit requirements, and compliance objectives.

Contact GxP Cellators

AI adoption can create new opportunities for pharmaceutical organizations, but it also requires appropriate controls over data, documentation, and decision-making. A structured, risk-based GxP audit can help identify weaknesses and support effective remediation.

If your organization needs assistance reviewing AI data integrity risks, training data traceability, model change documentation, or related GxP controls, contact GxP Cellators to discuss your requirements.

Contact: https://www.gxpcellators.com/contact/

14/10/2026
AI-Governance-ALCOA-and-Data-Integrity-1280x720.webp

Introduction

Artificial intelligence (AI) is becoming increasingly important in pharmaceutical manufacturing, laboratory operations, quality management, and other regulated life sciences activities. AI systems can help organizations analyse large datasets, identify patterns, support quality decisions, and improve operational efficiency. However, their use also creates new challenges related to data integrity, transparency, accountability, and regulatory compliance.

In GxP environments, reliable data is essential for maintaining product quality, patient safety, and regulatory confidence. This is where ALCOA+ principles become particularly important. These principles help organizations maintain complete, accurate, consistent, and reliable records throughout the data lifecycle.

When AI is used in a GxP-regulated process, auditors must assess more than the final output. They should also examine data sources, model development, access permissions, audit trails, change control, and ongoing system monitoring.

This guide explains what GxP auditors should check when reviewing AI governance, ALCOA+ compliance, and data integrity. It also explains how GxP Cellators supports organizations through specialized AI governance and data integrity auditing services.

What Is ALCOA+ and Why Does It Matter for AI?

ALCOA+ is a set of data integrity principles used to help ensure that records remain reliable, complete, and trustworthy. These principles are particularly relevant in pharmaceutical and other regulated environments where decisions may affect product quality and patient safety.

For AI applications, these principles should be considered across the entire data lifecycle, including data collection, preparation, model development, validation, deployment, and ongoing operation.

The Nine ALCOA+ Principles

  • Attributable: Data should clearly identify the person or system responsible for generating, modifying, or recording it.
  • Legible: Records should remain readable and understandable throughout their lifecycle.
  • Contemporaneous: Data should be recorded when the activity takes place, with appropriate timestamps.
  • Original: Records should be original or verified copies that preserve the required information.
  • Accurate: Data should correctly represent the activity, measurement, or observation.
  • Complete: All required data, relevant records, and associated metadata should be retained.
  • Consistent: Records should follow a logical sequence and remain consistent across systems.
  • Enduring: Data should be securely preserved for the required retention period.
  • Available: Records should be accessible for review, investigation, and regulatory inspection when needed.

AI systems can process large amounts of information, but processing data efficiently does not automatically make that data reliable. Therefore, organizations should establish controls to demonstrate how data is created, transformed, stored, accessed, and used by AI applications.

What Should GxP Auditors Check for AI Governance?

AI governance establishes how an organization manages, approves, monitors, and controls AI systems. A documented governance framework helps ensure that AI applications are used responsibly and remain appropriate for their intended purpose.

1. Documented AI Governance Framework

Auditors should verify whether the organization has an approved AI governance framework covering system selection, risk assessment, validation, deployment, monitoring, and retirement.

The framework should explain how AI-related risks are identified and managed. It should also define the approval process for introducing AI into regulated activities.

2. Roles and Responsibilities

Clear accountability is essential when AI supports GxP processes. Auditors should review whether responsibilities are assigned to quality assurance, IT, data science, system owners, and relevant business teams.

They should also check whether personnel understand their responsibilities for reviewing AI outputs and escalating unexpected results.

3. AI Risk Assessment

Not every AI application creates the same level of risk. An AI tool used for administrative support may have a different risk profile from a system that influences product release, laboratory decisions, or manufacturing controls.

Auditors should check whether risk assessments consider intended use, data sensitivity, system complexity, human oversight, and the potential consequences of incorrect outputs.

4. Change Control and Model Updates

AI models, datasets, configurations, and software components may change over time. These changes can affect system performance and the reliability of outputs.

Auditors should verify that significant changes are documented, assessed, approved, tested, and released through an appropriate change control process. Where necessary, the organization should also reassess model performance and validation status.

Training Data Integrity: Essential Audit Checks

Training data plays a major role in AI performance. Poor-quality, incomplete, inaccurate, or unsuitable data can affect the reliability of model outputs. Consequently, auditors should examine how training datasets are selected, prepared, reviewed, and maintained.

1. Data Sources and Traceability

Auditors should confirm that training data comes from identified and appropriate sources. Documentation should explain where the data originated, who supplied it, and whether its use is authorized.

Where relevant, the organization should maintain traceability between source records, processed datasets, and the final data used to develop or evaluate the model.

2. Data Completeness and Accuracy

Incomplete or inaccurate datasets may produce misleading results. Auditors should review whether data quality checks identify missing values, duplicate records, incorrect entries, and inconsistencies.

They should also verify that corrections and data exclusions are documented and justified rather than performed without appropriate oversight.

3. Data Preprocessing and Transformation

AI development often involves cleaning, filtering, labelling, normalizing, or transforming datasets. Each step can affect the information available to the model.

Auditors should check whether preprocessing methods are documented, reproducible, and appropriately reviewed. Important transformations should preserve traceability to the source data.

4. Bias and Representativeness

Training data should be appropriate for the intended application. If the dataset does not adequately represent the conditions in which the model will operate, the results may be unreliable.

Auditors should review whether the organization has assessed relevant data limitations, potential bias, and the suitability of the dataset for its intended use.

Operational Data Integrity: What Auditors Should Review

After an AI system is deployed, its operational data must remain controlled and traceable. Auditors should examine the records generated during routine use and determine whether the organization can reconstruct important activities when required.

1. Audit Trails and Event Logging

Audit trails and system logs can help establish who performed an action, when it occurred, and what changed. Auditors should verify that relevant events are recorded and that logs are protected against unauthorized modification or deletion.

They should also assess whether the organization reviews audit trails according to documented procedures and investigates relevant discrepancies.

2. Access Controls and User Permissions

Access controls help prevent unauthorized changes to data, configurations, and AI models. Auditors should review user roles, authentication measures, privileged access, and periodic access reviews.

Where applicable, they should verify that access permissions follow the principle of least privilege and that inappropriate access is removed promptly.

3. AI Outputs and Human Oversight

AI-generated outputs should be reviewed according to the risk and intended use of the application. In regulated activities, organizations should define when human review, verification, or approval is required.

Auditors should check whether users can understand the limitations of the system and whether unexpected or questionable outputs are investigated before being used in important decisions.

4. Data Retention and Availability

Organizations should retain required records for the applicable retention period and make them available for quality investigations or regulatory review.

Auditors should confirm that backup, restoration, archival, and retrieval procedures are documented and tested where appropriate. They should also check that retained records remain readable and usable.

Common AI Governance and Data Integrity Audit Findings

Several weaknesses can affect the reliability and compliance of AI applications in GxP environments. Common areas for review include:

  • Missing or incomplete AI governance policies.
  • Unclear ownership of AI systems and their outputs.
  • Insufficient documentation of training data sources.
  • Inadequate records of data preprocessing and transformation.
  • Missing, incomplete, or poorly reviewed audit trails.
  • Uncontrolled AI model or configuration changes.
  • Inadequate access controls and user permission reviews.
  • Limited evidence supporting model performance and intended use.
  • Incomplete procedures for investigating unexpected AI outputs.
  • Weak change control, corrective action, and follow-up processes.

These examples are potential audit findings, not a claim that every AI implementation has these deficiencies. Their relevance depends on the system, its intended use, and the applicable regulatory requirements.

Organizations should document each confirmed finding, assess its impact, identify the underlying cause, and establish appropriate corrective and preventive actions (CAPA).

How GxP Cellators Supports AI Governance and Data Integrity Audits

GxP Cellators provides specialized auditing and compliance support for organizations operating in regulated life sciences environments. Its AI governance and data integrity audit services can help companies assess whether appropriate controls, documentation, and oversight are in place for their AI applications.

AI Governance and Data Integrity Audit Services

Depending on the project scope and system requirements, support may include:

  • AI governance framework assessments.
  • ALCOA+ compliance reviews for AI systems.
  • Training data quality and traceability audits.
  • Operational data integrity audits.
  • Audit trail and event logging reviews.
  • User access control assessments.
  • AI system documentation and change control reviews.
  • Mock AI audits and inspection readiness support.
  • CAPA review, verification, and follow-up.

These activities can help organizations identify control weaknesses, improve documentation, and prioritize remediation before a formal inspection or internal quality review.

Why Choose GxP Cellators?

GxP Cellators focuses on practical auditing and compliance support for regulated organizations. Its approach can be tailored to the AI application, relevant risks, existing quality systems, and project objectives.

Key considerations include:

  • A risk-based approach suited to the intended use of the AI application.
  • Assessment of GxP processes, documentation, and data integrity controls.
  • Practical findings with clear recommendations for remediation.
  • Support for quality system improvements and CAPA follow-up.
  • Confidential handling of project information, subject to agreed arrangements.

Regulatory expectations differ according to the applicable jurisdiction, product, process, and intended use of the system. Therefore, organizations should assess relevant FDA, EMA, Health Canada, MHRA, WHO, and other applicable requirements rather than assume that one checklist covers every situation.

Best Practices for Maintaining ALCOA+ Compliance in AI Systems

Organizations can strengthen AI governance and data integrity by building appropriate controls into the entire system lifecycle.

  1. Define intended use: Document what the AI system is designed to do and identify the GxP processes it may affect.
  2. Assess risks: Evaluate potential consequences of inaccurate data, unreliable outputs, unauthorized changes, and system failure.
  3. Maintain data traceability: Preserve appropriate records showing where data originated and how it was transformed.
  4. Control changes: Review and approve significant changes to models, datasets, configurations, and supporting software.
  5. Protect audit trails: Ensure relevant events are recorded, retained, and reviewed according to approved procedures.
  6. Train personnel: Help users understand system limitations, data integrity responsibilities, and escalation procedures.
  7. Monitor performance: Establish appropriate monitoring and review processes to identify unexpected changes in performance.
  8. Perform periodic audits: Reassess controls as the system, data, risks, and regulatory expectations evolve.

These practices should be proportionate to risk and supported by documented procedures and evidence.

Frequently Asked Questions

1. What is ALCOA+ and how does it apply to AI?

ALCOA+ is a data integrity framework covering Attributable, Legible, Contemporaneous, Original, Accurate, Complete, Consistent, Enduring, and Available records. In AI systems, these principles help organizations assess the reliability and traceability of training data, operational data, and system-generated records.

2. What should GxP auditors check for AI governance?

GxP auditors should review the AI governance framework, assigned responsibilities, risk assessments, change control, model updates, documentation, and human oversight. They should also determine whether controls are appropriate for the system’s intended use and potential impact on GxP activities.

3. What should auditors check for training data integrity?

Auditors should examine data sources, traceability, completeness, accuracy, preprocessing documentation, and dataset suitability. They should also review how the organization assesses potential bias, records data transformations, and protects source information.

4. What should auditors check for operational AI data integrity?

Auditors should review audit trails, access permissions, timestamps, data retention, model changes, and the traceability of AI inputs and outputs. They should also assess whether unexpected results are investigated and whether records remain available for quality reviews and regulatory inspections.

5. Why are AI governance and data integrity audits important in pharmaceutical companies?

These audits help pharmaceutical companies identify weaknesses in data controls, documentation, system oversight, and change management. They can support risk reduction, improve inspection readiness, and provide evidence that AI applications are managed appropriately for their intended GxP use.

6. How does GxP Cellators support AI governance and data integrity audits?

GxP Cellators offers specialized audit support covering AI governance frameworks, ALCOA+ principles, training data quality, operational data integrity, audit trails, access controls, and CAPA follow-up. The scope can be tailored to the organization’s AI applications and compliance objectives.

7. How can I contact GxP Cellators for AI auditing services?

Visit the GxP Cellators contact page to discuss your AI governance, ALCOA+ compliance, and data integrity audit requirements.

Contact GxP Cellators

AI governance and data integrity are important considerations when AI systems support regulated activities. By reviewing data traceability, access controls, audit trails, change management, and human oversight, organizations can identify potential weaknesses and strengthen their compliance processes.

GxP Cellators provides auditing and compliance support to help life sciences organizations assess AI governance and data integrity controls. If your organization needs support with AI governance assessments, ALCOA+ reviews, or GxP data integrity audits, visit the GxP Cellators contact page to discuss your requirements.


13/10/2026
Audit-AI-Data-Integrity-1280x720.webp

Introduction

Data integrity is a fundamental requirement for maintaining GxP compliance in pharmaceutical, biotechnology, and life sciences organizations. As artificial intelligence (AI) becomes more common in regulated environments, companies must ensure that the data used to develop, train, validate, and operate AI systems remains accurate, complete, consistent, and traceable.

An AI system may process large amounts of information, identify patterns, support quality decisions, or assist with manufacturing and laboratory activities. However, unreliable data can affect the accuracy of its outputs and create potential compliance risks. Therefore, organizations need a structured approach to audit AI data integrity in a GxP environment.

An effective audit should examine both training data and operational data. It should also evaluate data governance, access controls, audit trails, model changes, data processing, and corrective actions.

GxP Cellators provides specialized AI auditing services to help pharmaceutical and life sciences organizations assess data integrity controls, identify compliance gaps, and strengthen their audit readiness.

Why Is AI Data Integrity Important in a GxP Environment?

GxP environments require organizations to maintain reliable records and follow documented procedures that support product quality, patient safety, and data reliability. When AI systems are introduced into these environments, the same principles must be considered throughout the data lifecycle.

For example, an AI application used to review laboratory results may produce unreliable recommendations if its training data contains incomplete or inaccurate records. Similarly, an AI system supporting pharmaceutical manufacturing may generate misleading outputs if operational data is modified without appropriate controls.

Poor AI data integrity can lead to several problems:

  • Inaccurate or inconsistent AI-generated outputs.
  • Incomplete or unreliable electronic records.
  • Unauthorized changes to data or model configurations.
  • Limited traceability of AI-generated recommendations.
  • Weak documentation and audit trail controls.
  • Difficulty investigating deviations and data integrity incidents.
  • Increased risk during regulatory inspections.

Consequently, organizations should evaluate AI data integrity as part of their broader GxP quality management and computerized system governance processes.

Step 1: Understand the AI System and Its Intended Use

Before beginning an audit, auditors should understand how the AI system operates and how it supports regulated activities. The intended use determines the type of data involved, the risks associated with the system, and the controls that need to be reviewed.

Start by documenting the following information:

  • What is the intended use of the AI system?
  • Which GxP processes does it support?
  • What data is used to train the model?
  • What operational data does the system receive?
  • How is the data processed, transferred, and stored?
  • Does the AI system influence product quality, laboratory results, or other regulated decisions?
  • Who is responsible for system oversight and data management?

Auditors should also review relevant system documentation, risk assessments, validation records, standard operating procedures (SOPs), and data flow diagrams.

Understanding the system first helps auditors identify critical data points and determine which controls require closer examination.

Step 2: Assess Training Data Integrity

Training data plays an important role in determining how an AI model learns and performs. If the data is incomplete, inaccurate, outdated, or unsuitable for its intended purpose, the model may produce unreliable results.

A training data audit should examine the origin, quality, suitability, and traceability of the datasets used to develop the AI system.

Verify Data Sources and Reliability

Auditors should establish where training data originated and whether the organization has documented its sources. Data collected from laboratory systems, manufacturing equipment, quality management systems, historical records, or external providers should have appropriate provenance documentation.

The audit should determine whether the organization can explain how the data was obtained and whether its use is appropriate for the intended application.

Review Completeness and Representativeness

Training datasets should be assessed for missing values, duplicate records, inconsistencies, and other quality issues. Auditors should also evaluate whether the dataset adequately represents the conditions under which the AI system is expected to operate.

Where relevant, the review should consider potential bias, unusual data patterns, and limitations that could affect model performance.

Examine Data Preprocessing

AI development may involve data cleaning, transformation, normalization, filtering, or annotation. These activities should be documented so that the organization can explain how the original data was changed before it was used for training.

Auditors should check whether preprocessing steps are reproducible, justified, and subject to appropriate review.

Confirm Data Provenance and Lineage

Data provenance identifies where data came from, while data lineage helps explain how it moved through different systems and processing stages.

An effective audit should verify that the organization maintains suitable records to trace datasets from their original sources through preparation, model training, and subsequent use.

Step 3: Assess Operational Data Integrity

Training data is only one part of the audit. Operational data must also remain reliable after an AI system is deployed.

Operational data may include user inputs, laboratory results, manufacturing information, model outputs, system logs, and records generated during routine use.

Review Audit Trails

Auditors should determine whether relevant system activities are recorded and whether the audit trails provide sufficient information to reconstruct important events.

Depending on the system, this may include data creation, modification, deletion, access, processing, and model-related changes.

The audit should also verify whether audit trails are protected against unauthorized alteration and reviewed according to documented procedures.

Evaluate Access Controls

Access controls help prevent unauthorized users from viewing, modifying, exporting, or deleting regulated data.

Auditors should review user roles, permissions, authentication controls, privileged access, and periodic access reviews. They should also determine whether access rights follow the principle of least privilege.

Shared accounts and excessive permissions may reduce accountability and make investigations more difficult.

Examine AI Outputs and Traceability

Organizations should be able to identify the relevant input data, system version, and processing context associated with important AI outputs.

Where appropriate, records should identify the user or system responsible for an action and document how the output was reviewed or used in a regulated decision.

Auditors should also determine whether human review is required for critical decisions and whether that review is documented.

Review Data Backup and Recovery

Data backups help protect information against accidental deletion, system failures, and other incidents. However, having a backup process alone is not sufficient.

Auditors should examine backup schedules, storage protections, recovery procedures, and evidence of restoration testing. They should also verify that recovered data remains complete and usable.

Step 4: Review Data Governance and ALCOA+ Principles

A documented data governance framework helps organizations define responsibilities and maintain control over data throughout its lifecycle.

Auditors should check whether responsibilities for data ownership, quality monitoring, access management, incident reporting, and record retention are clearly defined.

They should also review whether employees receive appropriate training and whether procedures explain how data integrity issues must be reported, investigated, and resolved.

Apply ALCOA+ Principles to AI Data

ALCOA+ is a widely used framework for evaluating data integrity in regulated environments. Its principles provide a useful basis for assessing the reliability of relevant AI records.

The audit should consider whether data is:

  • Attributable: The person or system responsible for an action can be identified.
  • Legible: Records remain readable and understandable throughout their retention period.
  • Contemporaneous: Data is recorded at the time the activity takes place.
  • Original: Original records or verified true copies are retained as required.
  • Accurate: Records correctly reflect the activity or observation.
  • Complete: Relevant data, metadata, and associated records are retained.
  • Consistent: Records follow the expected sequence and remain internally consistent.
  • Enduring: Data remains preserved throughout the required retention period.
  • Available: Records can be retrieved when needed for review or inspection.

For AI applications, auditors should consider how these principles apply to source datasets, preprocessing records, operational inputs, generated outputs, audit trails, and relevant metadata.

Step 5: Review Model Changes and Data Lifecycle Controls

AI systems may change over time as datasets are updated, models are retrained, software components are modified, or system configurations are adjusted.

These changes can affect system performance and may introduce new data integrity risks.

Auditors should review whether model and system changes are documented, assessed for risk, reviewed, tested, and approved before implementation where required.

The audit should also examine:

  • Version control for models and relevant datasets.
  • Records of model training and retraining.
  • Change control procedures.
  • Impact assessments for significant changes.
  • Testing and validation evidence.
  • Approval records and implementation history.
  • Monitoring for unexpected changes in system performance.

Organizations should define suitable controls based on the AI system’s intended use and its potential impact on GxP processes. Changes that may affect product quality, patient safety, or data reliability require particular attention.

Step 6: Identify Compliance Gaps and Develop a Remediation Plan

Once the audit is complete, the findings should be documented and assessed according to their potential impact.

Not every observation presents the same level of risk. Therefore, organizations should prioritize issues based on factors such as data criticality, potential impact on product quality, patient safety, regulatory compliance, and the reliability of decisions supported by the AI system.

A structured remediation process should include the following activities:

  1. Document each finding with supporting evidence.
  2. Assess the potential impact and associated risk.
  3. Identify the underlying cause of significant issues.
  4. Assign corrective and preventive actions (CAPA).
  5. Define action owners, responsibilities, and target dates.
  6. Implement approved corrective actions.
  7. Verify that the actions have been completed effectively.
  8. Maintain records and escalate unresolved high-risk issues.

For example, if an audit identifies incomplete documentation of training data preprocessing, the organization may need to update procedures, reconstruct available records, introduce review controls, and verify that the revised process is followed consistently.

A clear remediation plan helps turn audit observations into measurable improvements rather than leaving findings unresolved.

Common Challenges During AI Data Integrity Audits

Organizations may encounter several challenges when auditing AI systems in regulated environments.

Limited data traceability: Data may pass through several applications, databases, and processing tools, making it difficult to establish a complete history.

Insufficient documentation: Training data preparation, model changes, or operational decisions may not be documented consistently.

Unclear accountability: Responsibilities may be divided between IT teams, data scientists, quality assurance, and external technology providers.

Weak access management: Excessive permissions or shared accounts can reduce accountability and increase the risk of unauthorized changes.

Inadequate change control: Model updates may be introduced without a sufficient assessment of their impact on the intended GxP use.

Incomplete remediation: Organizations may close audit findings without verifying whether the underlying problem has been resolved.

Addressing these challenges requires cooperation between quality assurance, IT, data management, validation, and business teams.

How GxP Cellators Supports AI Data Integrity Audits

GxP Cellators provides specialized AI auditing services for pharmaceutical companies and other regulated life sciences organizations. Its approach focuses on reviewing data integrity controls, evaluating compliance risks, and identifying practical opportunities for improvement.

AI data integrity audit support may include:

  • Training data quality and provenance audits.
  • Operational data integrity assessments.
  • Data governance framework reviews.
  • Audit trail and access control reviews.
  • Data backup and recovery assessments.
  • Model change control and documentation reviews.
  • Mock AI audits and inspection readiness support.
  • CAPA verification and follow-up assessments.

GxP Cellators takes a risk-based approach tailored to the AI application, its intended use, and the relevant GxP processes. The audit scope can consider applicable expectations from authorities such as the FDA, EMA, Health Canada, and MHRA, depending on the organization’s markets and regulatory obligations.

The objective is to provide practical findings that help organizations understand weaknesses, prioritize remediation, and strengthen their compliance processes.

Why Choose GxP Cellators for AI Auditing Services?

Selecting an auditing partner with an understanding of both GxP requirements and AI-related risks can help organizations evaluate complex systems more effectively.

GxP Cellators supports organizations through a structured audit approach that focuses on evidence, risk assessment, documentation, and actionable recommendations.

Key benefits include:

  • A risk-based approach aligned with the intended use of the AI application.
  • Review of training and operational data controls.
  • Assessment of data governance, audit trails, and access management.
  • Identification of potential compliance gaps.
  • Practical recommendations for corrective actions.
  • Support for CAPA follow-up and audit readiness.
  • Confidential handling of proprietary business and system information, subject to agreed arrangements.

An independent assessment can help organizations gain a clearer understanding of their AI data integrity controls and determine where improvements are needed.

Conclusion

Auditing AI data integrity in a GxP environment requires more than checking whether data is accurate. Organizations must evaluate the complete data lifecycle, including source selection, training data preparation, operational processing, audit trails, access controls, governance, and model changes.

A structured, risk-based audit helps identify weaknesses before they develop into more serious quality or compliance concerns. In addition, documented corrective actions and effectiveness checks help ensure that identified gaps are addressed appropriately.

GxP Cellators supports pharmaceutical and life sciences organizations with specialized AI data integrity audits and related compliance assessments. To discuss your requirements and explore suitable AI auditing services, visit the contact page below.

Contact GxP Cellators: https://www.gxpcellators.com/contact/
Frequently Asked Questions

1. What is AI data integrity?

AI data integrity means maintaining the accuracy, completeness, consistency, traceability, and reliability of data used to train, validate, and operate AI systems. In GxP environments, these controls help support trustworthy records and reliable regulated processes.

2. How is training data integrity assessed?

Training data integrity is assessed by reviewing data sources, completeness, representativeness, preprocessing documentation, potential bias, and data provenance. Auditors also evaluate whether the organization can trace datasets through relevant preparation and training activities.

3. How is operational data integrity assessed?

Operational data integrity is assessed by examining audit trails, access controls, data processing, output traceability, model change documentation, backup procedures, and recovery testing. The scope depends on the system’s intended use and associated risks.

4. What are the ALCOA+ principles in AI data integrity?

ALCOA+ principles describe key characteristics of reliable data: attributable, legible, contemporaneous, original, accurate, complete, consistent, enduring, and available. They can help auditors evaluate relevant AI records and data management controls.

5. Why are audit trails important for AI systems in GxP?

Audit trails help organizations reconstruct relevant activities by recording important events and changes. When appropriately configured and reviewed, they support accountability, investigations, data integrity assessments, and regulatory inspection readiness.

6. How can organizations address AI data integrity gaps?

Organizations should document findings, assess their risks, identify root causes, assign corrective and preventive actions, and define responsible owners and timelines. They should also verify the effectiveness of completed actions and retain supporting evidence.

7. How does GxP Cellators support AI data integrity audits?

GxP Cellators provides support through training data quality audits, operational data integrity assessments, data governance reviews, audit trail evaluations, access control reviews, backup and recovery assessments, mock audits, and CAPA follow-up.

8. How can I contact GxP Cellators for AI data integrity audit support?

Visit the GxP Cellators contact page at https://www.gxpcellators.com/contact/ to discuss your AI data integrity audit requirements and explore relevant auditing support.
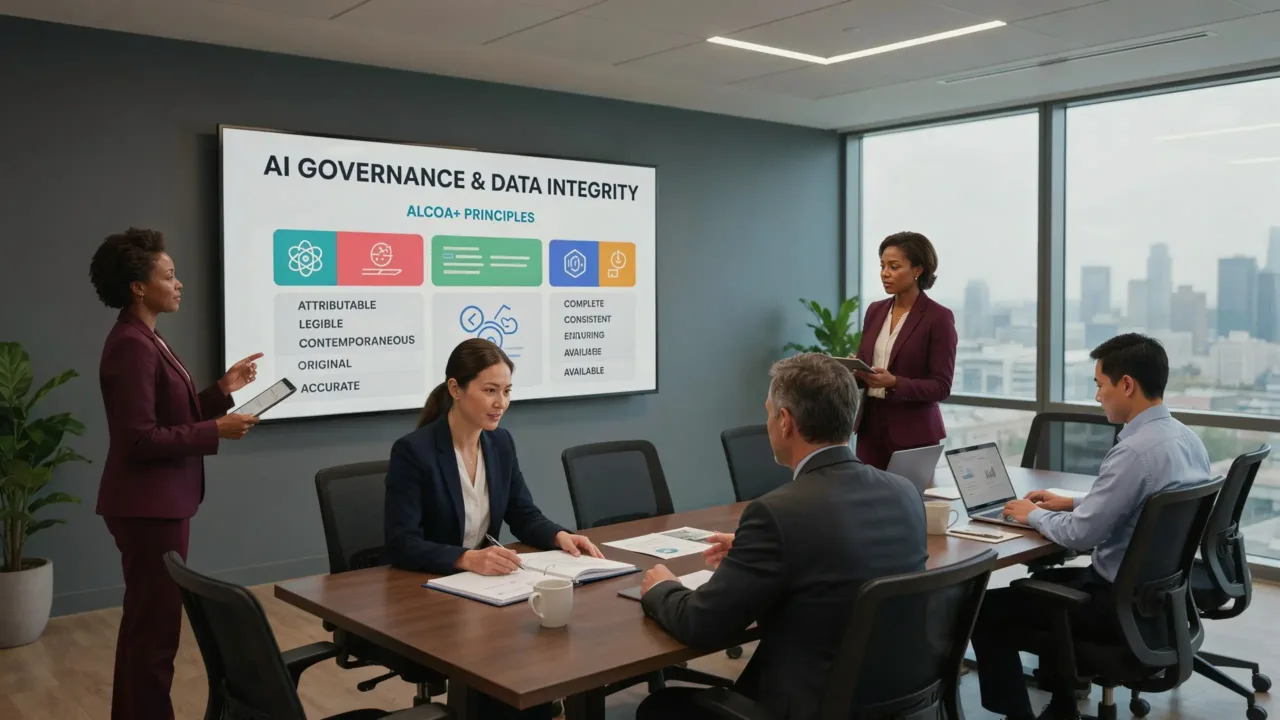

13/10/2026
AI-Governance-Audit-Checklist-1280x720.webp

Introduction

Artificial intelligence (AI) is becoming increasingly important in pharmaceutical manufacturing, quality management, clinical research, laboratory operations, and regulatory processes. However, using AI in a regulated environment also introduces risks related to data integrity, system reliability, patient safety, and regulatory compliance.

An AI governance audit checklist helps pharmaceutical companies evaluate whether their AI systems are managed responsibly throughout their lifecycle. It provides a structured way to review governance policies, risk assessments, human oversight, change control, vendor management, and documentation.

In GxP environments, AI governance should also align with applicable quality management systems, computerised system validation or assurance practices, data integrity expectations, and risk-based controls. The appropriate controls depend on the intended use of the AI system and its potential impact on product quality, patient safety, and data reliability.

GxP Cellators provides specialized auditing support for organizations seeking to strengthen their AI governance practices, identify compliance gaps, and improve inspection readiness.

What Is an AI Governance Audit?

An AI governance audit is a systematic assessment of the policies, procedures, responsibilities, controls, and documentation used to manage AI systems. It examines whether an organization has appropriate oversight of how AI solutions are selected, developed, tested, deployed, monitored, updated, and retired.

For pharmaceutical companies, the audit should consider how AI interacts with regulated processes. For example, an AI tool used to organize routine administrative information may have a different risk profile from a system that supports laboratory result interpretation, manufacturing decisions, or product quality assessments.

The purpose is not simply to confirm that an AI system works technically. Instead, the audit evaluates whether the organization can demonstrate appropriate control, traceability, accountability, and ongoing oversight.

Why Is AI Governance Important for Pharmaceutical Companies?

Pharmaceutical companies must maintain reliable processes and trustworthy records. Introducing AI without clear governance can create gaps in accountability, documentation, and risk management.

A structured governance program helps organizations:

  • Define accountability for AI-related decisions.
  • Identify and prioritize risks associated with AI applications.
  • Maintain appropriate human review of critical outputs.
  • Control changes to models, software, data, and configurations.
  • Evaluate third-party AI providers and service arrangements.
  • Protect sensitive information and maintain data integrity.
  • Establish monitoring and escalation procedures.
  • Prepare evidence for internal audits and applicable regulatory inspections.

Importantly, AI governance does not replace validation, qualification, or established quality controls. Instead, it helps coordinate these activities within a documented, risk-based management framework.

AI Governance Audit Checklist for Pharmaceutical Companies

The following checklist provides seven essential areas to review during an AI governance audit. Organizations should adapt these questions to their AI applications, quality systems, and applicable regulatory obligations.

1. AI Governance Framework

A documented governance framework establishes how AI systems are evaluated, approved, managed, and monitored across the organization.

During the audit, review the following questions:

  • Is there a documented AI governance policy or framework?
  • Has senior management approved the framework?
  • Does it define the scope of AI applications covered?
  • Does it address AI systems used in GxP activities?
  • Are approval and escalation processes clearly documented?
  • Is the framework reviewed periodically?
  • Are relevant policies updated when business processes or regulatory expectations change?

What auditors should verify: Review the approved policy, associated procedures, governance meeting records, and evidence of periodic review. Confirm that the framework applies to relevant AI systems rather than existing only as a high-level policy.

2. Roles and Responsibilities

Effective AI governance requires clear accountability. Quality assurance, regulatory affairs, IT, data science, operations, and business teams may all contribute to the oversight of an AI system.

The audit should determine whether:

  • AI system owners are formally identified.
  • Quality and compliance responsibilities are documented.
  • Approval authority is clearly assigned.
  • An AI oversight committee or equivalent governance body exists where appropriate.
  • Committee membership reflects the required technical and quality expertise.
  • Personnel receive suitable training.
  • Responsibilities are communicated to internal teams and relevant external partners.

What auditors should verify: Examine responsibility matrices, job descriptions, committee charters, training records, and meeting minutes. Check whether personnel understand their responsibilities when an AI system produces unexpected or potentially harmful results.

3. AI System Inventory and Classification

A complete AI inventory helps an organization understand which systems it uses and where governance controls are required. Without an accurate inventory, unapproved or undocumented AI applications may be overlooked.

Review whether:

  • A centralized inventory of relevant AI systems is maintained.
  • Each system has a defined owner and intended purpose.
  • The inventory identifies the system’s supplier or developer.
  • GxP relevance has been assessed.
  • Systems are classified according to risk and business impact.
  • New AI applications are assessed before deployment.
  • Model versions and significant configuration changes are traceable.
  • Retired or replaced systems are documented appropriately.

What auditors should verify: Compare the official inventory with information from IT, quality, laboratory, manufacturing, and other relevant departments. Where appropriate, also review approved software lists and supplier records to identify systems missing from the governance process.

4. AI Risk Assessment

Risk assessment is a central part of pharmaceutical AI governance. The level of control should reflect the system’s intended use, complexity, limitations, and potential impact on product quality, patient safety, and data integrity.

The audit checklist should include these questions:

  • Has each relevant AI system undergone a documented risk assessment?
  • Is the intended use clearly defined?
  • Are potential failure modes and foreseeable misuse considered?
  • Are risks to data integrity, privacy, and system reliability assessed?
  • Is the potential impact on GxP decisions evaluated?
  • Are high-risk applications subject to appropriate additional controls?
  • Are mitigation measures documented and approved?
  • Are risks reassessed following significant changes or incidents?

What auditors should verify: Review risk assessment reports, approval records, mitigation plans, and evidence that identified controls have been implemented. Confirm that risk classifications are supported by documented reasoning rather than assigned arbitrarily.

5. Change Control and AI Model Updates

AI systems may change through software releases, model updates, revised training data, configuration changes, or changes to their intended use. These changes can affect system performance and reliability.

The audit should establish whether:

  • AI systems are covered by an appropriate change control process.
  • Proposed changes are assessed before implementation.
  • Model and software versions are recorded.
  • Updates undergo suitable testing and approval.
  • The potential impact on validated or qualified states is evaluated.
  • Significant changes trigger risk reassessment where necessary.
  • Rollback or recovery arrangements are defined when appropriate.
  • Emergency changes are documented and reviewed.

What auditors should verify: Trace a sample change from its initial request through impact assessment, testing, approval, implementation, and post-implementation review. Check whether the process captures changes made by external AI providers as well as internal teams.

6. Human Oversight and AI Output Review

Human oversight is particularly important when AI outputs influence regulated decisions. Personnel should understand the system’s limitations and know when an output requires additional investigation.

During the audit, assess whether:

  • Human review requirements are documented.
  • Personnel can challenge or override AI recommendations where appropriate.
  • Critical decisions receive the required level of review.
  • Overrides and interventions are recorded when necessary.
  • Users understand the system’s intended use and limitations.
  • Procedures explain how to handle unexpected outputs.
  • Escalation arrangements exist for potentially incorrect results.
  • Appropriate training is provided to system users and reviewers.

What auditors should verify: Review relevant procedures, training records, sample decision records, and documented exceptions. Determine whether human oversight is meaningful or whether employees routinely accept AI outputs without appropriate evaluation.

7. AI Vendor and Supplier Management

Third-party AI tools can introduce additional risks because organizations may have limited visibility into model development, data handling, software updates, and supplier controls.

The audit should assess whether:

  • AI suppliers undergo documented qualification or assessment.
  • Supplier risks are evaluated according to intended use.
  • Responsibilities between the organization and supplier are defined.
  • Contracts or quality agreements address relevant quality obligations where appropriate.
  • Suppliers provide sufficient technical and compliance documentation.
  • Data security and confidentiality requirements are addressed.
  • Supplier changes are communicated and assessed.
  • Ongoing performance monitoring is established.
  • Supplier audits are conducted when justified by risk and applicable requirements.

What auditors should verify: Examine supplier assessments, contracts, service descriptions, security documentation, change notifications, and available audit evidence. Confirm that the organization understands which controls remain its responsibility even when an AI service is outsourced.

Additional Areas to Include in an AI Governance Audit

Although the seven checklist areas provide a strong foundation, pharmaceutical organizations should also review supporting controls that affect AI reliability and compliance.

Data Integrity and Documentation

Review how AI-related data is collected, processed, stored, and retained. Where relevant, confirm that records are attributable, legible, contemporaneous, original or appropriately verified, and accurate. Also evaluate access controls, audit trails, record retention, and traceability of important decisions.

The applicable data integrity controls should reflect the system’s intended use and the relevant GxP requirements.

Performance Monitoring and Incident Management

AI governance should continue after deployment. Organizations need procedures for monitoring performance, identifying unexpected behavior, documenting incidents, and escalating significant concerns.

Check whether performance indicators, review frequencies, acceptance criteria, and escalation thresholds are defined where appropriate. Verify that incidents and recurring issues are investigated and that corrective and preventive actions (CAPA) are implemented when required.

Documentation and Audit Trail Review

AI governance decisions should be supported by suitable evidence. Depending on the application, this may include requirements, risk assessments, testing records, approvals, model versions, monitoring reports, and incident investigations.

Auditors should confirm that records are controlled, accessible to authorized personnel, and sufficiently detailed to reconstruct important decisions.

Common Findings During AI Governance Audits

Organizations may encounter several recurring weaknesses when introducing AI into regulated processes.

  • Missing governance procedures: AI tools are adopted without a clear approval and oversight framework.
  • Incomplete inventories: Departments use AI applications that are not recorded centrally.
  • Weak risk assessments: Assessments do not adequately consider the intended use or impact on GxP activities.
  • Uncontrolled updates: Model or software changes are introduced without appropriate impact assessment.
  • Insufficient human oversight: Personnel rely on AI outputs without following defined review procedures.
  • Limited supplier oversight: Organizations lack adequate information about third-party controls or change management.
  • Poor documentation: Decisions, exceptions, approvals, and corrective actions cannot be reconstructed reliably.
  • Inadequate monitoring: There is no clear process for detecting performance issues after deployment.

These findings should be evaluated in context. Their significance depends on the application, applicable requirements, and potential impact. Organizations should document each finding, assess its risk, assign responsibility, and establish appropriate corrective actions.

How GxP Cellators Supports AI Governance Audits

GxP Cellators supports pharmaceutical and life sciences organizations with auditing and compliance services designed to help identify weaknesses and strengthen governance practices.

Its AI governance audit support can include:

  • AI governance framework assessments.
  • Reviews of roles, responsibilities, and oversight arrangements.
  • AI system inventory and classification reviews.
  • AI risk assessment reviews.
  • Change control and model update reviews.
  • Human oversight process assessments.
  • AI vendor and supplier audit support.
  • Mock AI audits and inspection-readiness assessments.
  • Documentation and data integrity reviews.
  • CAPA verification and follow-up.

The scope of each engagement should be tailored to the organization’s AI applications, regulatory environment, and identified risks.

Why Choose GxP Cellators?

GxP Cellators focuses on practical audit support for regulated organizations. Its approach emphasizes identifying control weaknesses, reviewing available evidence, and providing actionable recommendations.

Organizations can discuss their requirements, including relevant FDA, EMA, Health Canada, MHRA, or WHO expectations, depending on their operations and applicable regulatory obligations.

The goal is to help companies understand their current governance position, prioritize remediation activities, and improve oversight of AI systems used in regulated processes.

To discuss your requirements, visit the GxP Cellators Contact Page.

Frequently Asked Questions

1. What should be included in an AI governance audit checklist?

An AI governance audit checklist should cover the governance framework, roles and responsibilities, AI system inventory, risk assessment, change control, human oversight, vendor management, data integrity, documentation, and ongoing performance monitoring. The checklist should be tailored to the intended use and risk of each AI system.

2. Why is AI governance important for pharmaceutical companies?

AI governance helps pharmaceutical companies maintain oversight of AI applications and manage risks involving product quality, patient safety, data integrity, and regulatory compliance. It establishes clear responsibilities, documented controls, and processes for monitoring and managing AI systems throughout their lifecycle.

3. Who should be part of an AI oversight committee?

Depending on the organization’s size and AI applications, an oversight committee may include representatives from quality assurance, regulatory affairs, IT, data science, information security, operations, and relevant business functions. Members should have suitable expertise, clearly defined responsibilities, and appropriate decision-making authority.

4. How often should an AI governance audit be conducted?

The audit frequency should be based on risk, applicable requirements, changes to the AI environment, and the organization’s quality system. Higher-risk applications may require more frequent review. Significant incidents, supplier changes, model updates, or changes in intended use may also trigger additional assessments.

5. What is the difference between AI governance and AI validation?

AI governance defines the policies, responsibilities, oversight, and controls used to manage AI systems. AI validation or an appropriate assurance approach evaluates whether a system meets its intended requirements and is suitable for its intended use. Both activities can be important in regulated environments, but they serve different purposes.

6. How does GxP Cellators support AI governance audits?

GxP Cellators offers AI governance audit support that may include framework assessments, risk assessment reviews, inventory reviews, change control assessments, vendor audit support, mock audits, and CAPA follow-up. The engagement scope can be tailored to the organization’s requirements.

7. How can a pharmaceutical company prepare for an AI governance audit?

Start by identifying relevant AI systems and their intended uses. Gather governance policies, risk assessments, system inventories, change records, supplier documentation, training records, and monitoring evidence. Assign responsible personnel, review open CAPAs, and address significant gaps before the audit.

Contact GxP Cellators for AI Governance Audit Support

A structured AI governance audit checklist can help pharmaceutical companies identify weaknesses before they develop into larger quality or compliance concerns. By reviewing governance responsibilities, system risks, change control, human oversight, and supplier management, organizations can establish a more controlled approach to AI adoption.

GxP Cellators provides specialized auditing support to help organizations assess AI governance practices, identify potential gaps, and plan appropriate improvements.

Contact GxP Cellators: https://www.gxpcellators.com/contact/

13/10/2026
AI-Governance-and-Data-Integrity-Audits-in-GxP-1280x720.webp

Introduction

Artificial intelligence (AI) is increasingly being used across pharmaceutical manufacturing, laboratory operations, clinical research, quality management, and regulatory processes. Although AI can improve efficiency and support better decision-making, its use in regulated environments also introduces new compliance challenges.

In 2026, AI governance and data integrity remain important considerations for organizations operating under Good Manufacturing Practices (GMP), Good Laboratory Practices (GLP), Good Clinical Practices (GCP), and other GxP requirements. Companies must understand how AI systems are developed, validated, monitored, and maintained throughout their lifecycle.

AI governance and data integrity audits in GxP help organizations assess whether AI applications operate under appropriate controls and whether the data they process remains reliable, traceable, and protected from unauthorized changes.

GxP Cellators provides specialized auditing and compliance support to help pharmaceutical and life sciences organizations identify risks, review documentation, and strengthen their AI governance frameworks.

This guide explains AI governance, data integrity requirements, essential audit checklist items, common compliance risks, and how professional AI auditing services can support GxP compliance.

What Is AI Governance in GxP?

AI governance is the framework of policies, procedures, responsibilities, and oversight mechanisms used to manage AI systems throughout their lifecycle. In a regulated environment, this framework should ensure that AI applications are appropriately assessed, documented, monitored, and controlled.

Unlike general business applications, AI systems used in GxP processes may influence product quality, laboratory results, clinical data, manufacturing decisions, or patient safety. Therefore, organizations should establish governance controls that reflect the intended use and potential risks of each application.

Key Elements of GxP AI Governance

An effective AI governance framework should include the following elements:

  • AI system inventory: Maintain a documented list of AI tools and applications used in regulated processes.
  • Risk assessment: Evaluate the potential impact of each AI system on product quality, data integrity, patient safety, and regulatory compliance.
  • Defined responsibilities: Assign clear accountability for system ownership, validation, monitoring, and approval.
  • Governance oversight: Establish appropriate review and escalation processes for AI-related risks.
  • Change control: Assess and document model updates, configuration changes, and modifications to data sources.
  • Human oversight: Define when qualified personnel must review, approve, or override AI-generated recommendations.
  • Vendor management: Evaluate third-party AI providers, their documentation, security controls, and support arrangements.
  • Lifecycle monitoring: Review system performance and suitability throughout its operational life.

These controls help organizations understand how AI systems are used and ensure that important decisions remain appropriately governed.

What Is Data Integrity for AI Systems?

Data integrity refers to the accuracy, completeness, consistency, and reliability of data throughout its lifecycle. For AI applications, this includes the data used to train, configure, test, and operate a model, as well as the inputs and outputs generated during routine use.

Poor data quality can lead to unreliable AI recommendations, inaccurate predictions, and potentially unsuitable decisions. In regulated environments, these problems may also affect the reliability of records used to demonstrate compliance.

Important Data Integrity Controls for AI

Organizations should evaluate several areas when reviewing AI data integrity:

  • Training data quality: Confirm that data is suitable for its intended purpose and has appropriate quality controls.
  • Audit trails: Maintain suitable records of relevant inputs, outputs, user activities, and system changes.
  • Access controls: Restrict system and data access according to assigned responsibilities.
  • Model documentation: Record relevant model versions, configurations, updates, and approvals.
  • Data traceability: Maintain sufficient information to understand where data originated and how it was processed.
  • Backup and recovery: Establish appropriate measures to protect important records and support recovery.
  • Output review: Define how AI-generated results are reviewed, verified, and approved when necessary.

These controls should be proportionate to the system’s intended use and risk. Not every AI application requires identical controls, but regulated organizations should be able to justify their approach.

Understanding ALCOA+ Principles in AI Data Integrity

ALCOA+ is a widely used framework for evaluating data integrity in regulated industries. Its principles can help organizations assess whether records generated or processed by AI systems are trustworthy.

The principles include:

  • Attributable: Records identify who performed an action or which system generated the information.
  • Legible: Records remain readable and understandable throughout their retention period.
  • Contemporaneous: Information is recorded at the time the activity occurs or in accordance with applicable requirements.
  • Original: Original records or appropriately verified true copies are retained as required.
  • Accurate: Data and records correctly represent the activity or result.
  • Complete: Relevant data, including necessary metadata and associated records, is retained.
  • Consistent: Records follow an appropriate chronological and logical sequence.
  • Enduring: Records remain accessible and protected throughout their required retention period.
  • Available: Records can be retrieved when needed for review, investigation, or inspection.

During AI data integrity audits, these principles can help auditors assess input records, model outputs, audit trails, and supporting documentation. However, applying ALCOA+ alone does not establish full compliance; organizations must also consider applicable regulations, system requirements, and intended use.

AI Governance and Data Integrity Audit Checklist

A structured checklist helps organizations evaluate whether their AI systems have suitable governance and data integrity controls. The following areas can support internal assessments and audit preparation.

1. AI Governance Review

Check whether:

  • A documented AI governance framework is available.
  • All relevant AI systems are identified in an inventory.
  • Roles and responsibilities are clearly assigned.
  • AI-related risks are included in appropriate quality risk management activities.
  • Procedures exist for approving new AI applications.
  • Model updates and significant changes follow documented change control.
  • Human oversight requirements are clearly defined.
  • AI-related incidents are recorded, investigated, and escalated.
  • Third-party AI tools are assessed before use.
  • Periodic reviews evaluate whether systems remain suitable for their intended purpose.

2. Data Integrity Review

Check whether:

  • AI inputs and outputs are recorded appropriately for their intended use.
  • Relevant audit trails are enabled and protected.
  • User access is controlled and periodically reviewed.
  • Training and operational data have suitable quality controls.
  • Data sources and transformations are sufficiently traceable.
  • Model changes are documented and approved.
  • Data integrity issues can be detected and investigated.
  • Records meet applicable ALCOA+ expectations.
  • Backup, recovery, and retention arrangements are documented.
  • AI-generated results are reviewed when required by risk or procedure.

3. Validation and Documentation Review

AI systems used in regulated processes should be assessed according to their intended use, potential risks, and applicable requirements.

Auditors may review:

  • User requirements and intended-use documentation.
  • Risk assessments and validation plans.
  • Testing records and acceptance criteria.
  • Model configuration and version history.
  • Change control and approval records.
  • Procedures for monitoring system performance.
  • Training records for relevant personnel.
  • Incident management and corrective action documentation.

The exact documentation required depends on the application, its impact on regulated activities, and the applicable regulatory framework.

Common AI Governance and Data Integrity Audit Findings

Organizations may encounter several recurring weaknesses when reviewing AI applications in GxP environments.

Incomplete AI System Inventory

Some organizations introduce AI tools through different departments without maintaining a complete inventory. As a result, quality teams may not know which applications influence regulated processes.

A documented inventory, supported by periodic reviews, can improve visibility and accountability.

Weak Change Control

AI models, software configurations, and connected data sources may change over time. If changes are introduced without appropriate assessment and documentation, the organization may lose confidence in the system’s validated state.

A risk-based change control process should determine which changes require additional testing, review, approval, or revalidation.

Insufficient Data Traceability

When organizations cannot explain where data originated or how an AI system processed it, investigating unexpected results becomes difficult.

Appropriate metadata, audit trails, and documented data flows can help establish traceability.

Unclear Human Oversight

AI-generated outputs should not automatically replace qualified human judgment in situations where review or approval is required.

Organizations should define responsibilities, escalation procedures, and review criteria according to the risks associated with each application.

Inadequate Vendor Oversight

Third-party AI platforms may introduce risks related to data access, system changes, documentation, and transparency.

Supplier assessments should consider relevant technical controls, contractual responsibilities, change notifications, and access to evidence needed to support compliance.

How to Prepare for an AI Governance and Data Integrity Audit

Preparation should begin before an internal or external audit is scheduled. A structured approach helps organizations identify weaknesses and collect relevant evidence.

Step 1: Identify AI Applications

Create an inventory of AI systems used in manufacturing, laboratory operations, quality management, clinical research, and other relevant processes.

Step 2: Assess Compliance Risks

Evaluate each application according to its intended purpose and potential impact on product quality, patient safety, data integrity, and regulated decisions.

Step 3: Review Policies and Procedures

Check whether governance, validation, access control, change management, incident handling, and data integrity procedures adequately address the relevant AI applications.

Step 4: Examine Supporting Evidence

Review system documentation, risk assessments, testing records, audit trails, training records, approvals, and supplier documentation.

Step 5: Identify and Prioritize Gaps

Document identified weaknesses, assess their potential impact, and prioritize corrective actions based on risk.

Step 6: Develop a CAPA Plan

Establish corrective and preventive actions (CAPA) with assigned owners, target dates, and clear completion criteria. Verify that completed actions address the identified problems.

Step 7: Conduct Follow-Up Reviews

Review the effectiveness of implemented controls and confirm that unresolved issues are managed appropriately.

Regulatory Considerations for AI Governance in GxP

AI governance must be considered alongside the regulations and quality requirements applicable to the organization’s operations. Relevant considerations may include FDA requirements, European Medicines Agency (EMA) expectations, Health Canada requirements, MHRA guidance, and applicable World Health Organization (WHO) guidance.

The specific obligations depend on the application, jurisdiction, and regulated activity. For example, AI used in a manufacturing quality decision may require a different assessment from AI used for general administrative support.

Organizations should also evaluate applicable requirements for computerized systems, electronic records, data integrity, validation, risk management, and quality oversight.

Importantly, there is no single universal AI audit checklist that guarantees compliance in every GxP environment. Companies should assess applicable requirements and document how their controls address identified risks.

How GxP Cellators Supports AI Governance and Data Integrity Audits

GxP Cellators provides specialized auditing and compliance support for pharmaceutical and life sciences organizations seeking to strengthen governance over AI applications.

Its AI governance and data integrity audit services can help organizations evaluate existing controls, identify compliance gaps, and develop practical improvement plans.

Our AI Governance and Data Integrity Audit Services Include

  • AI governance framework assessments.
  • Data integrity audits for AI systems.
  • Training data quality audits.
  • AI model validation documentation reviews.
  • Human oversight process audits.
  • AI vendor and supplier audits.
  • Regulatory compliance reviews.
  • Mock AI audits.
  • CAPA verification and follow-up.

Why Choose GxP Cellators?

GxP Cellators focuses on a risk-based approach that considers the intended use of AI systems and their impact on regulated operations.

Organizations can benefit from:

  • Auditing support focused on GxP quality and compliance.
  • Assessments tailored to relevant AI applications.
  • Reviews of documentation, governance, and data integrity controls.
  • Practical findings and recommendations for addressing identified gaps.
  • Support for regulatory readiness and corrective action follow-up.
  • Appropriate confidentiality when handling proprietary business and system information.

An independent audit can help organizations understand where controls may need improvement before those weaknesses affect regulated operations.

Benefits of AI Governance and Data Integrity Audits

A well-planned audit can deliver benefits beyond identifying documentation gaps.

Improved regulatory readiness: Organizations can identify weaknesses before an inspection or formal assessment.

Stronger data reliability: Reviews can highlight weaknesses in data traceability, access controls, audit trails, and record management.

Better risk management: Risk-based assessments help organizations prioritize issues according to their potential impact.

Clearer accountability: Defined governance responsibilities make it easier to manage AI systems and investigate incidents.

More effective change management: Documented review and approval processes help maintain appropriate control over model updates and system modifications.

Stronger supplier oversight: Vendor assessments can improve visibility into third-party risks and supporting compliance evidence.

These benefits depend on implementing appropriate corrective actions and maintaining effective controls after the audit.

Frequently Asked Questions

1. What is AI governance in GxP?

AI governance in GxP is the framework of policies, procedures, risk assessments, and oversight mechanisms used to manage AI systems in regulated environments. It covers system inventory, responsibilities, change control, human oversight, supplier management, and ongoing monitoring.

2. What is data integrity for AI systems?

Data integrity for AI systems means ensuring that relevant data remains accurate, complete, consistent, traceable, and protected throughout its lifecycle. Controls may include access restrictions, audit trails, training data quality reviews, model documentation, and ALCOA+ principles.

3. Why are AI governance and data integrity audits important?

These audits help organizations identify weaknesses in AI oversight, data handling, documentation, validation, and change management. Addressing those weaknesses can improve regulatory readiness and help protect the reliability of information used in GxP processes.

4. What should an AI governance audit checklist include?

An AI governance audit checklist should cover system inventory, risk assessment, roles and responsibilities, change control, human oversight, supplier management, data integrity, validation documentation, audit trails, incident handling, and CAPA follow-up.

5. How does ALCOA+ apply to AI systems?

ALCOA+ provides data integrity principles that can be applied to relevant records associated with AI systems. Auditors can use these principles to assess attribution, readability, contemporaneous recording, originality, accuracy, completeness, consistency, durability, and availability.

6. How does GxP Cellators support AI governance and data integrity audits?

GxP Cellators provides AI governance framework assessments, AI data integrity audits, training data quality reviews, model validation documentation assessments, supplier audits, mock audits, regulatory compliance reviews, and CAPA follow-up support.

7. How can a pharmaceutical company prepare for an AI audit?

A pharmaceutical company can prepare by identifying AI applications, assessing risks, reviewing governance procedures, organizing validation and data integrity evidence, evaluating suppliers, and addressing identified gaps through documented corrective actions.

8. How can I contact GxP Cellators for AI auditing services?

Organizations interested in AI governance and data integrity audit support can contact GxP Cellators through its official contact page to discuss their requirements and potential compliance support.

Contact GxP Cellators

AI technologies can support pharmaceutical and life sciences operations, but their use in regulated environments requires appropriate governance, documentation, and data integrity controls.

By conducting structured AI governance and data integrity audits, organizations can identify weaknesses, strengthen oversight, and improve their readiness for regulatory review.

GxP Cellators supports organizations through specialized auditing services, risk-based assessments, documentation reviews, and CAPA follow-up.

Contact GxP Cellators: https://www.gxpcellators.com/contact/
Discuss your AI governance, data integrity, and GxP auditing requirements with the team to explore suitable support for your organization.


13/10/2026
Risk-Based-AI-CSV-Audits-1280x720.webp

Introduction

Artificial intelligence (AI) is becoming increasingly important in pharmaceutical manufacturing, biotechnology, clinical research, and other regulated industries. Organizations are using AI to analyze data, support quality decisions, improve processes, and automate specific activities. However, when AI systems are used in GxP-regulated environments, organizations must ensure that these technologies operate reliably and meet applicable compliance requirements.

Risk-based AI CSV audits help organizations evaluate computerized systems according to their potential impact on patient safety, product quality, data integrity, and regulatory compliance. Instead of applying the same audit approach to every system, this method directs attention and resources toward areas with the greatest potential risk.

Computerized System Validation (CSV) traditionally focuses on demonstrating that computerized systems perform as intended. AI-enabled systems can introduce additional challenges because their outputs may depend on training data, model design, configuration, ongoing monitoring, and changes over time.

Therefore, GxP organizations need a structured approach to AI CSV risk assessment and auditing. In this guide, GxP Cellators explains the key steps involved in planning, conducting, and maintaining risk-based AI CSV audits.

What Are Risk-Based AI CSV Audits?

Risk-based AI CSV audits are structured assessments that examine AI-enabled computerized systems according to their intended use, criticality, and potential impact on regulated operations.

The objective is to determine whether appropriate controls, validation evidence, documentation, and monitoring processes are in place. Auditors also evaluate whether organizations can identify, assess, and manage risks associated with AI functionality.

For example, an AI tool that helps organize non-critical administrative information may require a different level of oversight from an AI system that influences batch release decisions, laboratory results, or other product-quality activities.

A risk-based approach helps organizations establish proportionate controls without overlooking important compliance responsibilities.

Why Are AI CSV Audits Important in GxP Environments?

AI systems can introduce risks that are not always addressed adequately by conventional software testing alone. These risks may involve unreliable outputs, biased or incomplete training data, insufficient documentation, unauthorized changes, or limited traceability.

A structured audit can help organizations evaluate whether:

  • The AI system has a clearly defined intended use.
  • Its use within GxP processes has been appropriately assessed.
  • Validation activities reflect the system’s intended purpose and risks.
  • Data integrity controls protect records throughout their lifecycle.
  • AI-generated outputs are reviewed appropriately.
  • Changes to models, data, or configurations are controlled.
  • Responsibilities for system oversight are clearly assigned.

The audit approach should reflect the actual system and its regulated use rather than assuming that every AI application presents the same level of risk.

Step-by-Step Guide to Risk-Based AI CSV Audits

Step 1: Identify and Inventory AI Systems

The first step is to identify all AI-enabled systems used in GxP-regulated activities. Organizations may have AI functionality embedded in commercial software, laboratory platforms, manufacturing systems, analytics tools, or internally developed applications.

A complete inventory should include:

  • System name and description.
  • Intended use and business purpose.
  • Associated GxP processes.
  • System owner and relevant stakeholders.
  • Data sources and integrations.
  • Validation status and available documentation.
  • AI model or software components, where applicable.

This inventory provides the foundation for risk assessment and audit planning. It also helps organizations identify systems that may have been introduced without sufficient quality oversight.

Step 2: Perform an AI CSV Risk Assessment

Once the inventory is complete, organizations should evaluate the risks associated with each system. The assessment should consider both the potential consequences of system failure and the effectiveness of existing controls.

Important risk factors include:

Patient safety: Could an incorrect AI output influence a decision that affects patient safety?

Product quality: Could the system affect manufacturing parameters, laboratory results, quality investigations, or product release decisions?

Data integrity: Could AI processing compromise the accuracy, completeness, consistency, or traceability of GxP records?

Regulatory compliance: Could the system create gaps in validation evidence, documentation, access control, or required oversight?

System complexity: Does the system use changing models, multiple integrations, external data sources, or complex decision-making processes?

Organizations should document the rationale behind their risk ratings. A risk matrix can help compare systems consistently, although the final assessment should reflect the intended use and relevant controls.

Step 3: Prioritize Audits According to Risk

After assessing the risks, organizations can establish an audit schedule based on system criticality, previous findings, control effectiveness, and the consequences of failure.

A practical classification may include the following levels:

  • High-risk systems: Systems with significant potential effects on patient safety, product quality, or critical GxP decisions. These generally require stronger oversight and more frequent review.
  • Medium-risk systems: Systems with a meaningful but more limited impact, supported by appropriate controls. Periodic audits should verify that these controls remain effective.
  • Low-risk systems: Systems with limited impact on regulated activities. Audits may be less frequent, depending on the documented risk assessment and applicable procedures.

These categories are examples rather than universal regulatory classifications. Organizations should establish their own criteria and audit frequencies through approved quality procedures.

Audits should also be reconsidered after significant system changes, major incidents, recurring deviations, or new information that changes the risk profile.

Step 4: Define the Audit Scope

A clear audit scope helps ensure that the assessment covers the most important risks. The scope should be based on the system’s intended use, risk assessment, applicable requirements, and previous audit findings.

Depending on the system, the audit may examine:

  • Validation strategy and supporting evidence.
  • User requirements and functional specifications.
  • AI model documentation and intended-use limitations.
  • Training, testing, and operational data quality.
  • Access controls and data integrity safeguards.
  • Change management and configuration controls.
  • AI output review and human oversight.
  • Incident management and deviation handling.
  • Supplier documentation and third-party responsibilities.
  • Periodic review and ongoing performance monitoring.

Not every audit requires the same depth of investigation. High-risk functions may need more detailed testing, stronger evidence, and closer examination of how AI outputs influence regulated decisions.

Step 5: Conduct the AI CSV Audit

During the audit, auditors compare documented procedures with actual practices. They review evidence, interview relevant personnel, examine system records, and assess whether established controls work as intended.

A structured audit process should include:

  1. Reviewing system documentation and the approved validation approach.
  2. Confirming that the documented intended use matches actual use.
  3. Examining risk assessments and control measures.
  4. Checking validation evidence and test coverage.
  5. Reviewing data integrity, access controls, and audit trails where applicable.
  6. Evaluating change control and incident management.
  7. Assessing human oversight of AI-generated outputs.
  8. Recording findings with supporting evidence.

Audit findings should clearly explain the issue, the relevant evidence, the potential impact, and the required follow-up. This makes it easier for system owners and quality teams to prioritize corrective actions.

Step 6: Manage Findings Through CAPA

Identifying audit findings is only one part of the process. Organizations must also determine the underlying causes and implement appropriate corrective and preventive actions (CAPA).

For example, an audit may identify incomplete documentation for an AI model update. The immediate correction may involve completing the required records. However, the underlying cause could be an unclear change-control procedure or insufficient staff training.

An effective CAPA process should include:

  • Clear descriptions of findings.
  • Documented root-cause analysis.
  • Corrective and preventive action plans.
  • Assigned responsibilities and completion dates.
  • Assessment of potential effects on existing GxP records or decisions.
  • Verification that actions were implemented.
  • Effectiveness checks where appropriate.

Critical issues should be escalated through the organization’s established quality and compliance procedures. Closure should be supported by evidence rather than relying only on statements that corrective actions are complete.

Step 7: Monitor and Review AI Systems Continuously

AI CSV risk assessments should not remain unchanged throughout a system’s lifecycle. A system’s risk profile may change when new data sources are introduced, models are updated, workflows change, or the system is used for additional purposes.

Organizations should establish monitoring and periodic review processes that consider:

  • Changes to AI models and software components.
  • Data quality issues and unexpected outputs.
  • Deviations, incidents, and recurring complaints.
  • Changes in intended use or GxP impact.
  • Supplier updates and relevant service changes.
  • Outstanding audit findings and CAPA effectiveness.
  • New or revised regulatory expectations.

These reviews help organizations determine whether additional validation, risk assessment, or auditing is necessary.

Key Challenges in AI CSV Auditing

Although risk-based auditing can improve oversight, AI-enabled systems may present several challenges.

Limited Transparency

Some AI models are difficult to interpret. Organizations should therefore document their intended use, limitations, performance criteria, and decision-making boundaries as appropriate. Where full interpretability is not possible, alternative controls and documented oversight may be needed.

Training Data Quality

Incomplete, inaccurate, or unsuitable data can affect AI performance. Auditors should examine relevant data governance procedures, data suitability assessments, and controls over data changes.

Model and Software Changes

Updates can alter system behavior. Organizations should assess changes according to their potential impact and determine whether additional testing, validation, or approval is required.

Inadequate Documentation

Missing risk assessments, unclear responsibilities, or incomplete validation records can make it difficult to demonstrate that an AI system is controlled. Documentation should provide traceable evidence of decisions, testing, approvals, and ongoing oversight.

Third-Party AI Solutions

External software providers may control important elements of an AI solution. Organizations should evaluate supplier documentation, responsibilities, change notifications, and available evidence while retaining appropriate oversight of their own GxP use.

How GxP Cellators Supports Risk-Based AI CSV Audits

GxP Cellators provides auditing and compliance support for organizations working in regulated life sciences environments. Its risk-based AI CSV audit services can help organizations evaluate computerized systems, identify compliance gaps, and strengthen their validation and governance practices.

Depending on the project’s scope and requirements, support may include:

  • AI system inventory and risk assessment.
  • Risk-based audit planning.
  • Comprehensive AI CSV audits.
  • Pre-audit readiness assessments.
  • AI governance framework reviews.
  • Training data quality audits.
  • AI model validation documentation reviews.
  • Data integrity audits.
  • Mock inspection support.
  • CAPA verification and follow-up.

The objective is to provide practical findings that help organizations understand weaknesses, prioritize remediation, and maintain appropriate controls throughout the system lifecycle.

Why Choose GxP Cellators?

Organizations need an audit approach that considers both computerized system validation and the specific challenges of AI technology.

GxP Cellators focuses on risk-based assessments, actionable reporting, and compliance considerations relevant to regulated environments. Its services can support organizations preparing for audits, reviewing AI governance, or evaluating the effectiveness of existing validation controls.

The scope of any engagement should be agreed in advance, including the systems covered, applicable requirements, expected deliverables, and confidentiality arrangements.

To discuss your requirements, visit the GxP Cellators Contact Page.

Best Practices for Effective Risk-Based AI CSV Audits

Organizations can strengthen their audit programs by following these practical recommendations:

  • Maintain an up-to-date inventory of AI-enabled GxP systems.
  • Define documented, risk-based criteria for audit prioritization.
  • Establish clear ownership for validation, quality, and AI governance.
  • Maintain traceable evidence for risk assessments and validation activities.
  • Evaluate data integrity and human oversight controls.
  • Apply change management to model, software, and intended-use changes.
  • Track findings through a formal CAPA process.
  • Reassess risk after significant changes or incidents.
  • Review applicable regulatory guidance before defining compliance expectations.
  • Keep audit schedules proportionate to system risk and control effectiveness.

These practices help integrate AI CSV auditing into the wider pharmaceutical quality management system instead of treating it as a separate, one-time activity.

Frequently Asked Questions

1. What is a risk-based AI CSV audit?

A risk-based AI CSV audit evaluates AI-enabled computerized systems according to their potential impact on patient safety, product quality, data integrity, and regulatory compliance. It directs audit effort toward the most significant risks.

2. How is risk assessed for AI systems in GxP environments?

Risk is assessed by examining intended use, GxP impact, system complexity, data quality, AI outputs, existing controls, and the potential consequences of failure. Organizations should document the assessment and its rationale.

3. How often should high-risk AI systems be audited?

Audit frequency should be established through a documented risk assessment and approved quality procedures. High-risk systems generally require closer oversight, with additional reviews after significant changes, incidents, or emerging compliance concerns.

4. How are AI CSV audits different from traditional CSV audits?

Traditional CSV audits evaluate computerized system controls and evidence that the system performs as intended. AI CSV audits may also need to examine model-related risks, training data, output reliability, human oversight, and changes that affect AI behavior.

5. What documents are reviewed during an AI CSV audit?

Depending on the system, auditors may review intended-use documentation, risk assessments, user requirements, validation plans and reports, test evidence, data governance procedures, change-control records, supplier documentation, and CAPA records.

6. Why are data integrity audits important for AI systems?

AI systems may process large volumes of data and generate outputs that influence regulated decisions. Data integrity audits help assess whether relevant records remain accurate, complete, traceable, and protected against unauthorized changes.

7. How does GxP Cellators support risk-based AI CSV audits?

GxP Cellators offers support that may include AI system risk assessments, audit planning, AI CSV audits, governance reviews, validation documentation reviews, data integrity assessments, mock inspections, and CAPA follow-up.

8. How can an organization request AI CSV audit support?

Organizations can contact GxP Cellators through its official contact page to discuss their systems, compliance objectives, audit scope, and support requirements.

Conclusion

Risk-based AI CSV audits help GxP organizations evaluate AI-enabled systems in a structured and proportionate manner. By identifying critical systems, assessing potential risks, prioritizing audit activities, and monitoring corrective actions, organizations can strengthen oversight of AI technologies used in regulated operations.

An effective approach combines documented risk assessments, appropriate validation evidence, data integrity controls, change management, and ongoing monitoring. Because AI systems and their intended uses can evolve, organizations should review their controls throughout the system lifecycle.

GxP Cellators supports organizations seeking practical AI CSV auditing and compliance solutions. Visit the GxP Cellators Contact Page to discuss your risk-based AI CSV audit requirements.


13/10/2026
AI-and-CSV-validation-challenges-1280x720.webp

Introduction

Artificial intelligence (AI) is changing how pharmaceutical companies manage data, automate processes, analyse information, and support critical business decisions. However, introducing AI into regulated computerized systems also creates new challenges for Computerized System Validation (CSV) and GxP compliance.

Traditional CSV approaches focus on demonstrating that computerized systems consistently perform their intended functions. AI-based systems can behave differently because their outputs may depend on training data, model design, changing inputs, and algorithmic behaviour. As a result, pharmaceutical companies must carefully evaluate how these systems are validated, monitored, and maintained throughout their lifecycle.

Understanding AI and CSV validation challenges is essential for protecting data integrity, maintaining product quality, and supporting regulatory compliance. Companies must also establish appropriate documentation, risk management, change control, and human oversight procedures.

In this guide, GxP Cellators explains five major AI validation challenges and practical approaches for addressing them in pharmaceutical and other regulated life sciences environments.

What Is the Relationship Between AI and Computerized System Validation?

Computerized System Validation is a documented process used to demonstrate that a computerized system is suitable for its intended use. In pharmaceutical environments, validation helps ensure that systems operate reliably and protect product quality, patient safety, and data integrity.

AI can be integrated into various regulated activities, including quality control, manufacturing, laboratory analysis, pharmacovigilance, document review, and quality management systems.

For example, an AI-powered system might analyse laboratory results, identify unusual manufacturing patterns, or assist with reviewing quality records. If its output influences a GxP decision, the company must evaluate the system’s intended use and potential impact on regulated activities.

AI validation therefore requires more than testing conventional software functions. Organizations must also assess model performance, data quality, output variability, explainability, and the controls used to manage changes.

Challenge 1: Non-Deterministic AI Outputs

One of the major AI and CSV validation challenges is non-deterministic behaviour. Some AI systems may generate different outputs when given the same input, depending on model configuration, sampling methods, contextual information, or other technical factors.

For example, an AI tool used to summarize deviation reports might produce slightly different summaries for repeated requests. In a regulated environment, the company must determine whether those variations could affect the accuracy or reliability of the final decision.

How to Address Non-Deterministic Outputs

1. Define clear acceptance criteria

Organizations should establish measurable acceptance criteria based on the system’s intended use. These criteria should identify acceptable output variations and define which errors could affect product quality, patient safety, or data integrity.

2. Test the system across multiple runs

Testing should include repeated executions, representative inputs, boundary conditions, and challenging scenarios. This helps organizations understand how consistently the model performs under defined conditions.

3. Establish human review controls

Where AI outputs influence important GxP decisions, qualified personnel should review the results according to documented procedures. The level of review should reflect the associated risk.

4. Implement ongoing performance monitoring

Monitoring helps identify unexpected changes in output quality, accuracy, or consistency. Companies should document deviations from expected performance and investigate significant issues.

Challenge 2: Continuous Learning and Model Changes

Some AI systems can be updated or retrained using new data. Even when a model does not learn automatically during operation, developers may periodically release updated versions.

These changes can affect how the system processes information and produces results. Consequently, a model that performed acceptably during initial validation might behave differently after an update.

Uncontrolled changes can create compliance risks, particularly when the system supports manufacturing decisions, laboratory operations, quality investigations, or other GxP activities.

How to Manage Continuous Learning

1. Establish formal change control

Every relevant model update, configuration change, or modification to training data should be assessed through an appropriate change control process. The assessment should document the reason for the change and its potential impact.

2. Define revalidation triggers

Organizations should establish criteria for determining when additional testing or revalidation is necessary. Triggers may include significant changes to the model, intended use, underlying data, or risk profile.

3. Maintain model version records

Companies should document model versions, approval status, relevant configurations, and the associated validation evidence. This makes it easier to establish which version was used when a particular result was generated.

4. Monitor performance after changes

Following an approved update, organizations should verify that the system continues to meet its intended requirements. Monitoring should include relevant performance indicators and documented procedures for investigating unexpected results.

Challenge 3: Lack of Transparency and Explainability

Some AI models are difficult to interpret because their outputs result from complex relationships within the model. This can make it challenging for pharmaceutical companies to understand why a particular recommendation or prediction was generated.

For regulated organizations, unexplained outputs may create difficulties during internal audits, regulatory inspections, and quality investigations. Companies need sufficient information to evaluate whether an AI system is suitable for its intended use.

The level of explainability required depends on the system’s function, complexity, and potential impact on GxP decisions.

How to Improve AI Transparency

1. Document the model and its intended use

Validation documentation should describe the model’s purpose, intended users, relevant limitations, assumptions, and operating conditions. Where appropriate, organizations should also document the model’s architecture and key configuration details.

2. Establish explainability requirements

Companies should determine what information users need to understand and evaluate model outputs. For high-impact applications, this may include explanations of important contributing factors, known limitations, and conditions in which the model may perform poorly.

3. Implement human oversight

Qualified personnel should be able to review relevant outputs, identify questionable recommendations, and escalate concerns. Responsibilities for accepting, rejecting, or overriding AI recommendations should be clearly defined.

4. Maintain traceable records

Organizations should retain appropriate records of inputs, outputs, model versions, reviews, and decisions. These records support investigations and help demonstrate that the system operates under controlled conditions.

Challenge 4: Data Dependency and Data Integrity

AI models depend heavily on the quality, relevance, and representativeness of their data. Incomplete, inaccurate, outdated, or biased training data can reduce model performance and lead to unreliable results.

For pharmaceutical companies, data quality is particularly important when AI systems interact with laboratory records, manufacturing data, quality events, or regulated documentation.

Poor data governance can also make it difficult to demonstrate where information originated, whether it was modified, and how it was used by the system.

How to Address Data-Related Challenges

1. Validate training and input data

Organizations should define data quality requirements and evaluate whether datasets are appropriate for the intended application. Relevant checks may include completeness, accuracy, consistency, representativeness, and suitability.

2. Establish data governance procedures

Documented governance procedures should define data ownership, access permissions, review responsibilities, retention requirements, and processes for correcting identified errors.

3. Maintain data provenance

Companies should preserve appropriate information about data sources, transformations, preparation methods, and subsequent use. Traceability supports investigations and helps demonstrate how the model’s results were produced.

4. Apply data integrity controls

Access controls, audit trails, backup procedures, and other appropriate safeguards should be evaluated according to the system’s risks and applicable requirements.

5. Monitor data and model performance

Changes in source data or operating conditions may affect model reliability. Organizations should establish monitoring and investigation procedures for significant performance changes or suspected data integrity issues.

Challenge 5: Regulatory Uncertainty and Evolving Expectations

AI technology is developing rapidly, and regulatory expectations may vary according to the application, jurisdiction, and potential impact on regulated activities.

Pharmaceutical companies must determine how applicable requirements and established GxP principles apply to their AI-enabled systems. They should not assume that using a new technology removes the need for appropriate validation, documentation, risk management, or oversight.

Instead, organizations should adopt a risk-based approach that considers the system’s intended use and its potential effect on product quality, patient safety, and data integrity.

How to Address Regulatory Uncertainty

1. Monitor relevant regulatory developments

Companies should review applicable guidance and regulatory updates from authorities such as the FDA, EMA, Health Canada, and MHRA, where relevant to their operations.

2. Apply risk-based validation

Validation activities should be proportionate to the system’s intended use and associated risks. Systems that directly influence critical GxP decisions may require more extensive controls and evidence than lower-risk administrative applications.

3. Maintain complete documentation

Organizations should document requirements, risk assessments, testing, approvals, changes, deviations, and ongoing monitoring activities as appropriate.

4. Review supplier and third-party controls

When an AI solution is supplied by an external vendor, companies should evaluate the vendor’s documentation, security controls, change notification practices, and ability to support validation activities.

5. Seek qualified compliance guidance

Specialist support can help organizations identify gaps, clarify validation responsibilities, and develop an appropriate compliance strategy for their AI-enabled systems.

How GxP Cellators Helps Address AI and CSV Validation Challenges

GxP Cellators supports regulated organizations with GxP auditing and compliance-related services. Companies evaluating AI-enabled computerized systems may benefit from a structured review of their validation approach, documentation, data controls, and governance processes.

The scope of any engagement should be tailored to the system, intended use, applicable requirements, and risks identified.

AI and CSV Audit Support Services

GxP Cellators can support relevant review activities, including:

  • AI CSV validation strategy reviews.
  • Computerized system validation documentation reviews.
  • AI model validation audits.
  • Training data quality audits.
  • Data integrity audits.
  • Human oversight process reviews.
  • Regulatory compliance reviews.
  • Mock inspection support.
  • Corrective and Preventive Action (CAPA) verification and follow-up.

Why Choose GxP Cellators?

Risk-based approach: Reviews can be tailored to the system’s intended use and potential GxP impact.

Practical recommendations: Audit findings can help organizations identify weaknesses and prioritize corrective actions.

Regulatory awareness: Applicable expectations from relevant authorities can be considered within the agreed audit scope.

Documentation focus: Reviews can assess whether validation records, change control documentation, and supporting evidence are appropriate for the intended use.

Confidentiality: Appropriate confidentiality arrangements are important when reviewing proprietary systems, sensitive records, and business information.

Organizations should confirm the scope, deliverables, and applicable regulatory coverage with GxP Cellators before engaging its services.

Best Practices for Validating AI-Enabled GxP Systems

Although each AI application requires an individual assessment, several practices can help pharmaceutical companies build a more effective validation strategy.

  1. Define the intended use: Clearly document what the AI system does, who uses it, and how its outputs influence regulated activities.
  2. Conduct a risk assessment: Identify possible effects on product quality, patient safety, data integrity, and regulatory compliance.
  3. Establish measurable requirements: Define performance expectations and acceptance criteria before testing begins.
  4. Evaluate data quality: Verify that the data used for training, testing, and operation is suitable for the intended purpose.
  5. Maintain lifecycle documentation: Record validation activities, approvals, model versions, changes, and relevant investigations.
  6. Control system changes: Use documented procedures to assess updates and determine whether additional testing is needed.
  7. Provide appropriate oversight: Ensure that qualified personnel understand the system’s limitations and their responsibilities.
  8. Monitor performance: Establish procedures for detecting unexpected results, investigating issues, and implementing corrective actions.

These practices help organizations integrate AI into regulated workflows without overlooking established CSV and GxP compliance principles.

Frequently Asked Questions

1. What are the key validation challenges for AI and CSV?

The main challenges include non-deterministic outputs, continuous learning, limited model transparency, data dependency, and evolving regulatory expectations. Organizations should address these through risk-based validation, documented change control, data governance, and ongoing performance monitoring.

2. How can non-deterministic AI outputs be validated?

Companies can define acceptance criteria that account for reasonable output variability, conduct repeated testing, evaluate challenging scenarios, and monitor performance. Where outputs influence critical GxP decisions, appropriate human review should also be established.

3. How can continuous learning be managed in AI systems?

Organizations should establish formal change control, maintain model version records, define revalidation triggers, and monitor performance after relevant changes. The approach should reflect whether the system learns during operation or receives periodic updates.

4. Why is data integrity important for AI validation in pharmaceutical companies?

AI systems rely on the quality and traceability of their data. Poor-quality or unreliable information can affect model performance and undermine confidence in its outputs. Appropriate data governance, access controls, audit trails, and provenance records help manage these risks.

5. How does GxP Cellators help address AI and CSV challenges?

GxP Cellators provides GxP auditing and compliance support that may include AI CSV strategy reviews, validation documentation reviews, model validation audits, data quality assessments, data integrity audits, and mock inspection support, depending on the agreed scope.

6. How can pharmaceutical companies prepare for AI-related regulatory inspections?

Companies should maintain clear documentation of intended use, risk assessments, validation testing, data governance, model changes, performance monitoring, and human oversight. They should also ensure that relevant personnel can explain the system’s role and limitations.

7. Where can I contact GxP Cellators for AI CSV validation support?

You can contact GxP Cellators through its official contact page to discuss your organization’s AI, CSV auditing, and GxP compliance requirements.

Conclusion

AI can offer significant benefits to pharmaceutical companies, but its integration into regulated computerized systems requires careful planning and ongoing oversight. Non-deterministic outputs, model changes, limited transparency, data quality issues, and evolving regulatory expectations can all affect validation activities.

By applying risk-based validation, maintaining reliable documentation, establishing appropriate change control, and monitoring system performance, organizations can better manage these challenges.

GxP Cellators can support relevant auditing and compliance review activities to help organizations identify potential gaps and strengthen their AI and CSV validation approach.

Need support with AI and CSV validation challenges? Visit the GxP Cellators to discuss your requirements.


Our Presence


Saskatchewan, Canada

Calgary, Canada

Toronto, Canada

North Carolina, USA

Frankfurt, Germany


Indiana, USA

Get in Touch


+1 (306) 715 -9460


Saskatchewan, Canada

https://www.gxpcellators.com


You cannot copy content of this page

Verified by MonsterInsights